Integrations: find the right screen
Every screen in this module, what each one is for, and where it lives. Use it to find the right screen quickly, and to confirm you are on the one a colleague means — several screens in this product have similar names and different jobs.
Screenshots come from a demonstration data set, so the figures are illustrative. Click any screenshot to open it at full resolution.
Acunetix
Dynamic application scanning.
AppScan
Application security testing, static and dynamic.
Burp Suite
Dynamic application testing. Findings arrive against the URL that was tested.
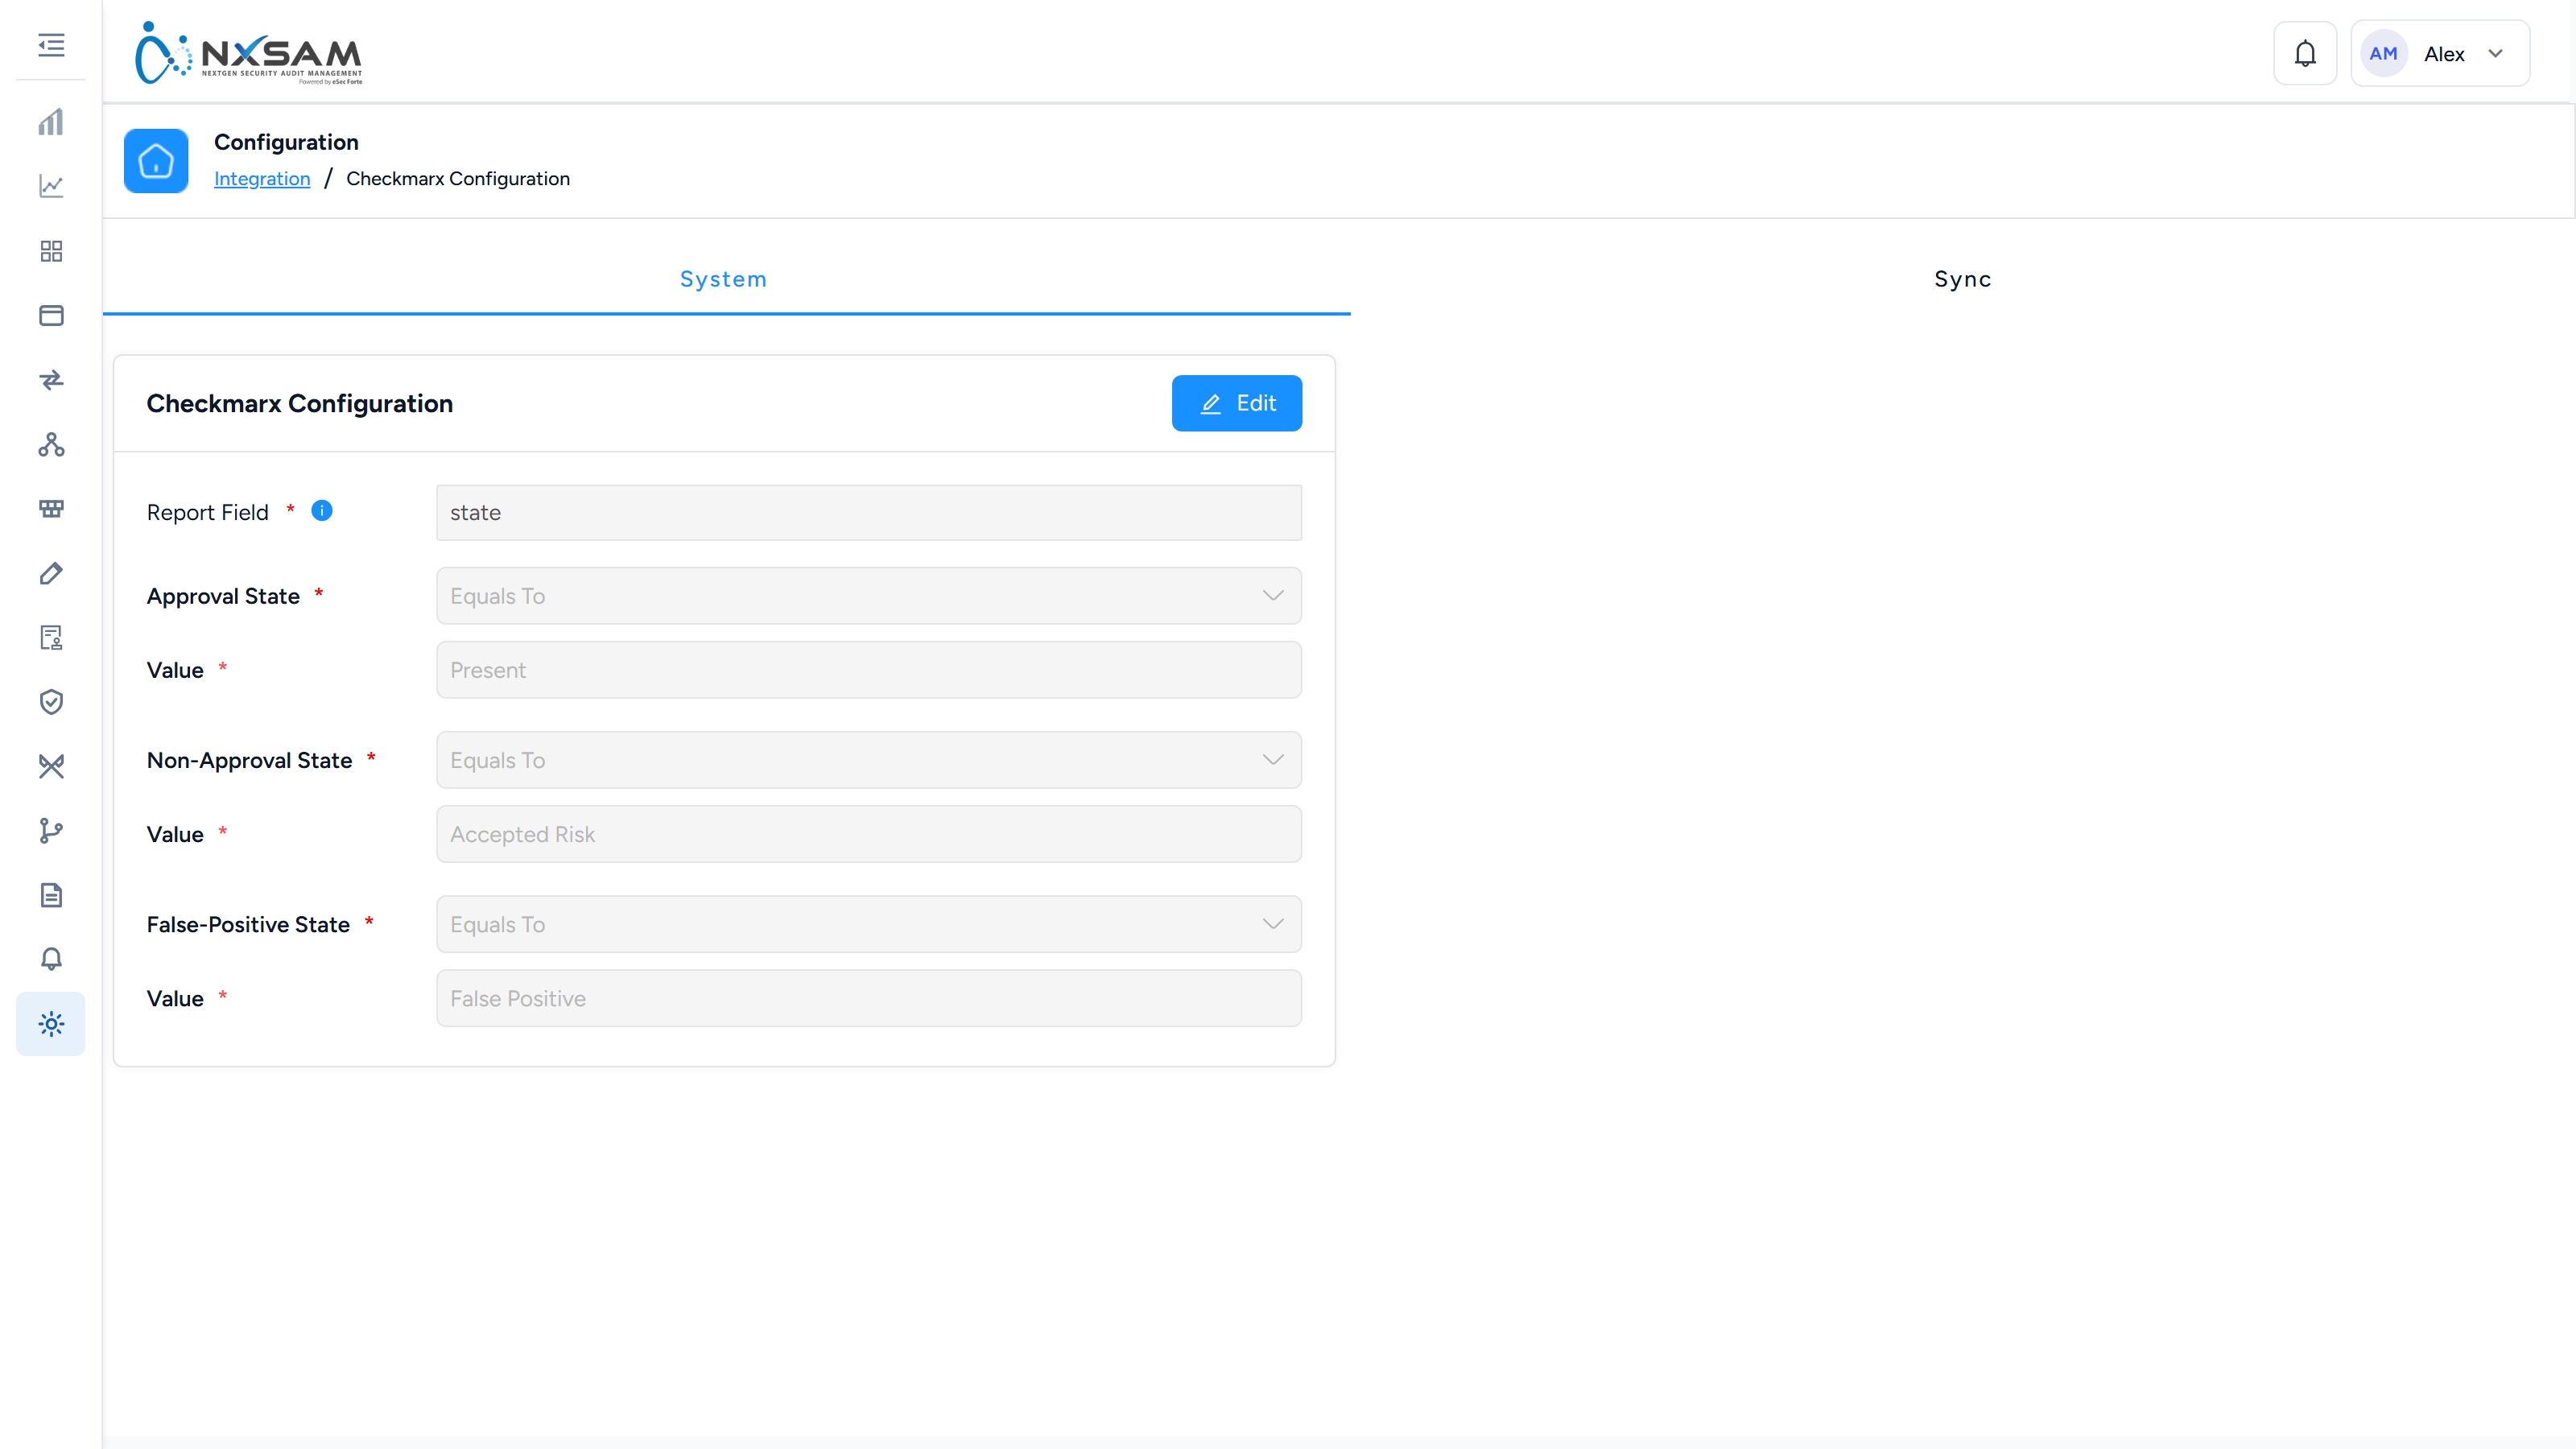
Checkmarx
Static application security testing. Projects map to NxSAM applications.
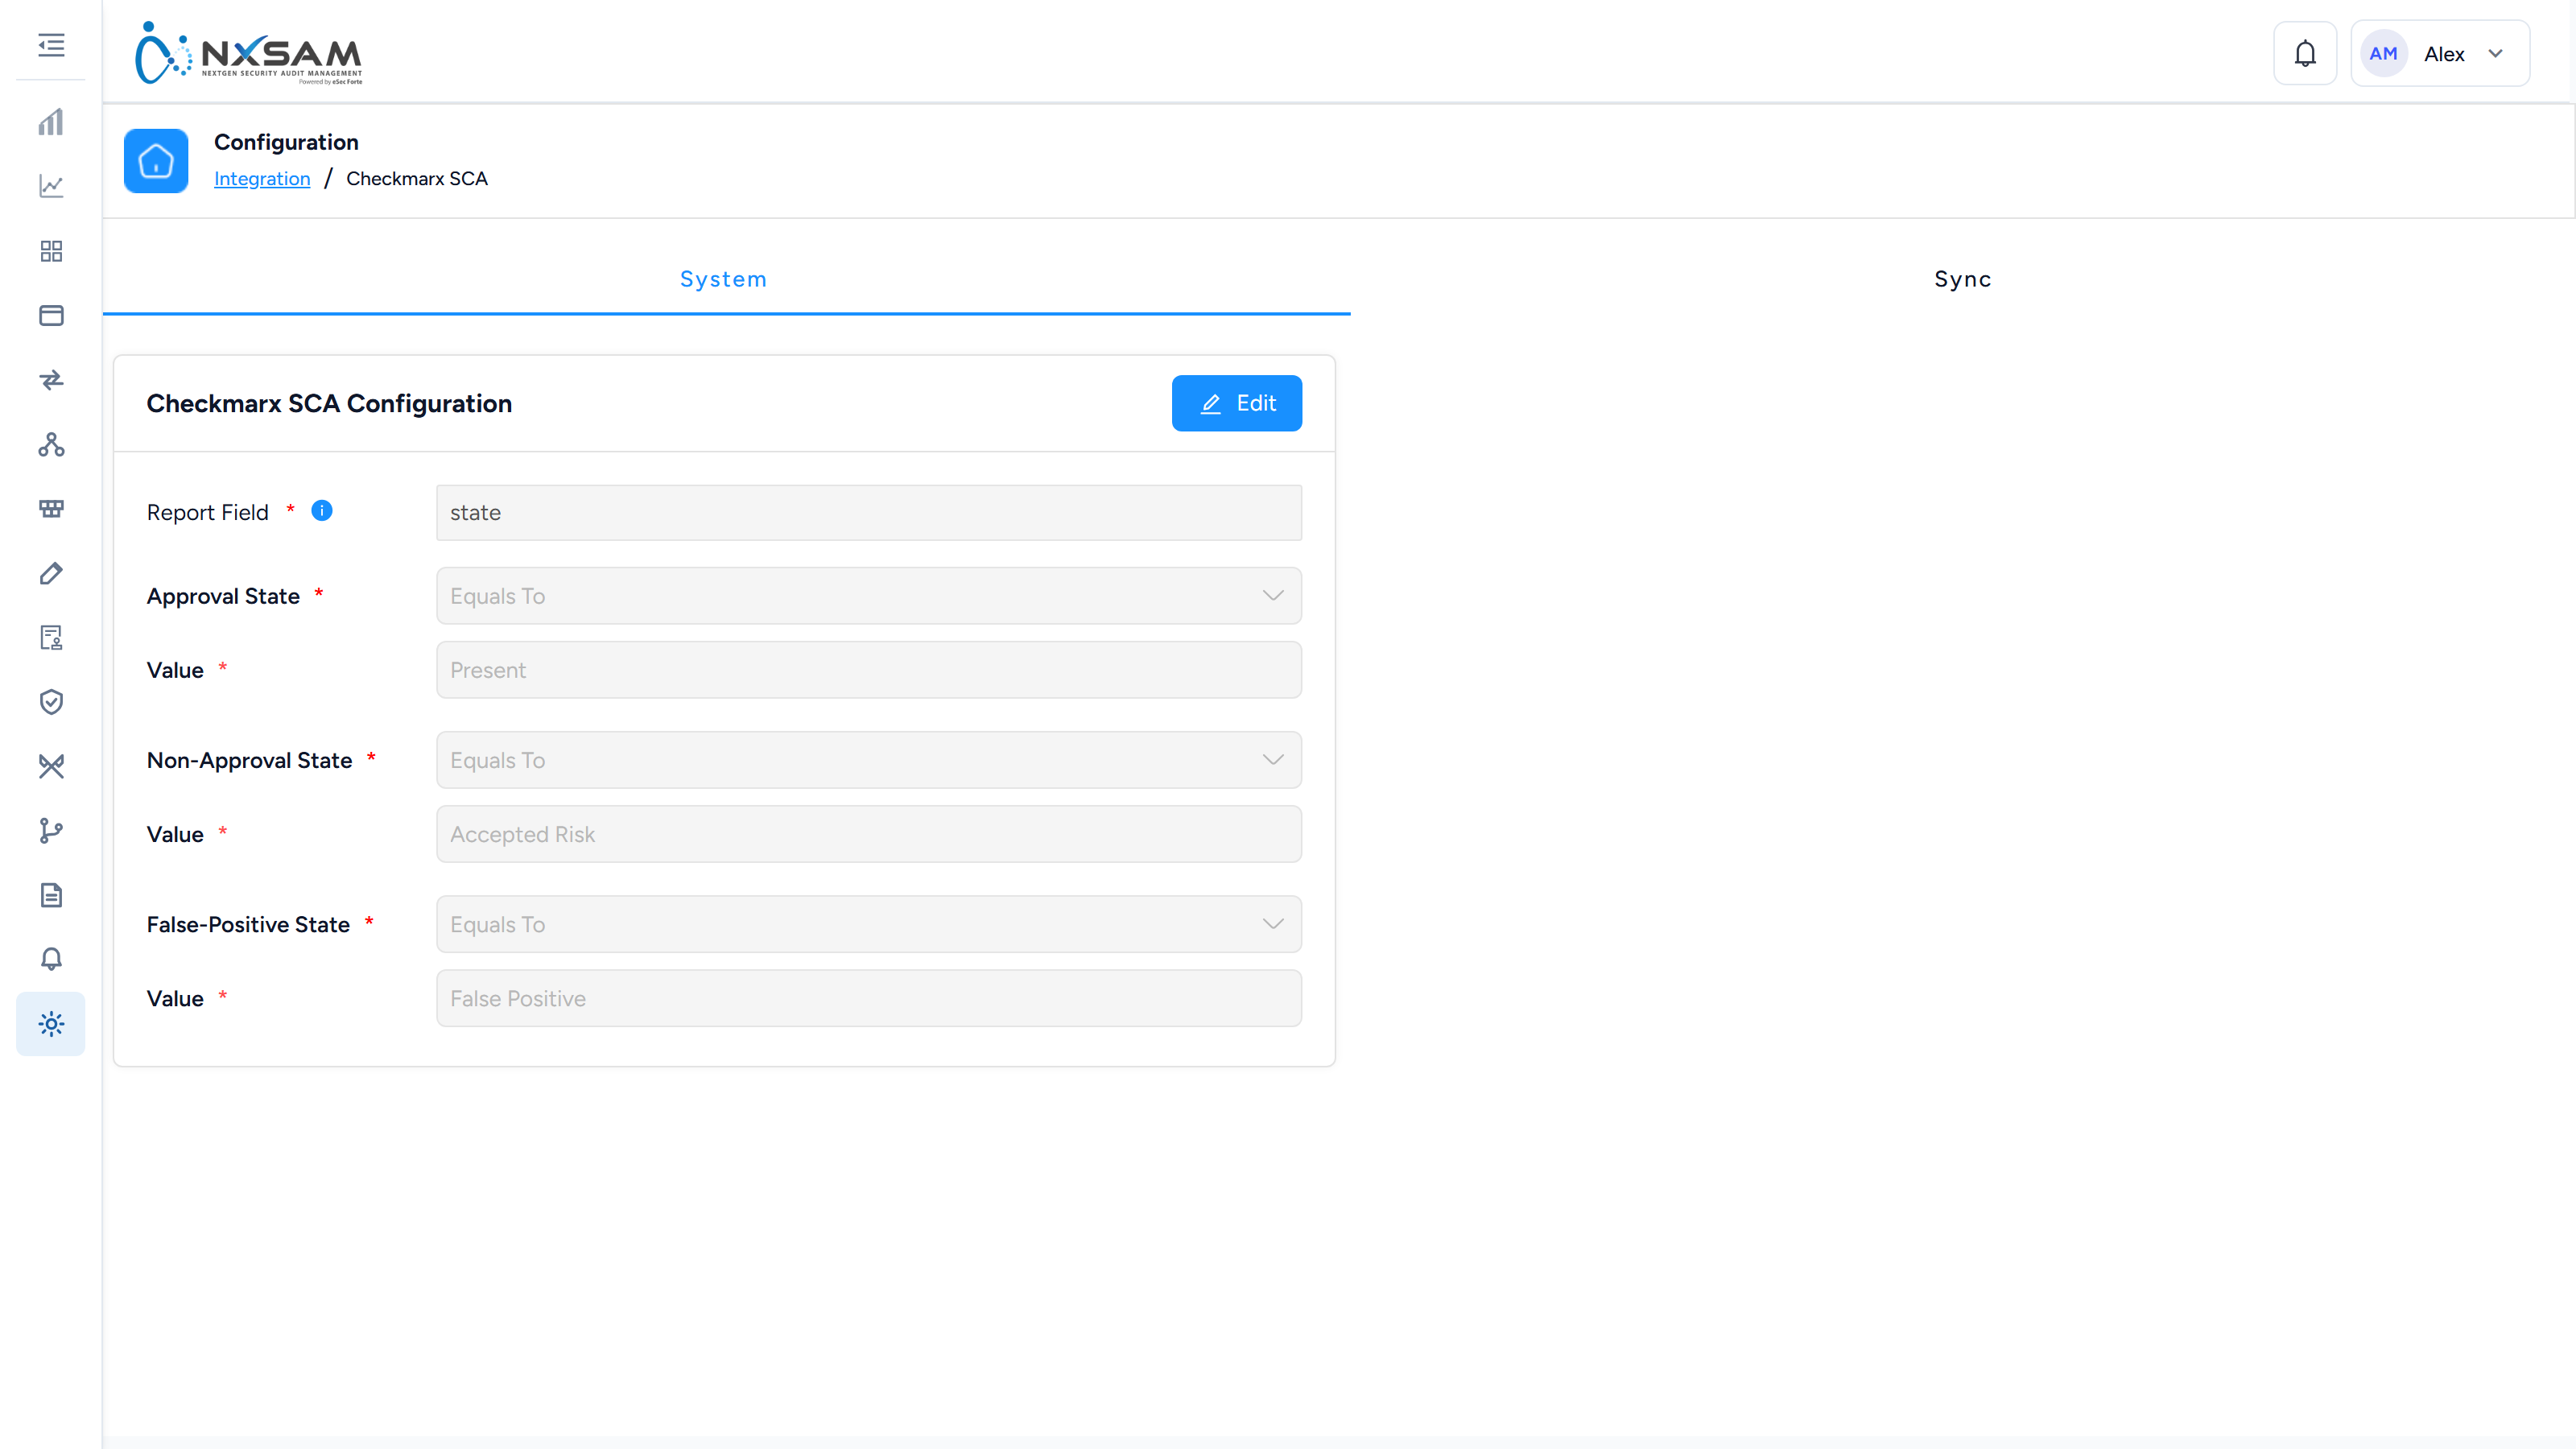
Checkmarx SCA
Software composition analysis — third-party libraries and their known vulnerabilities.
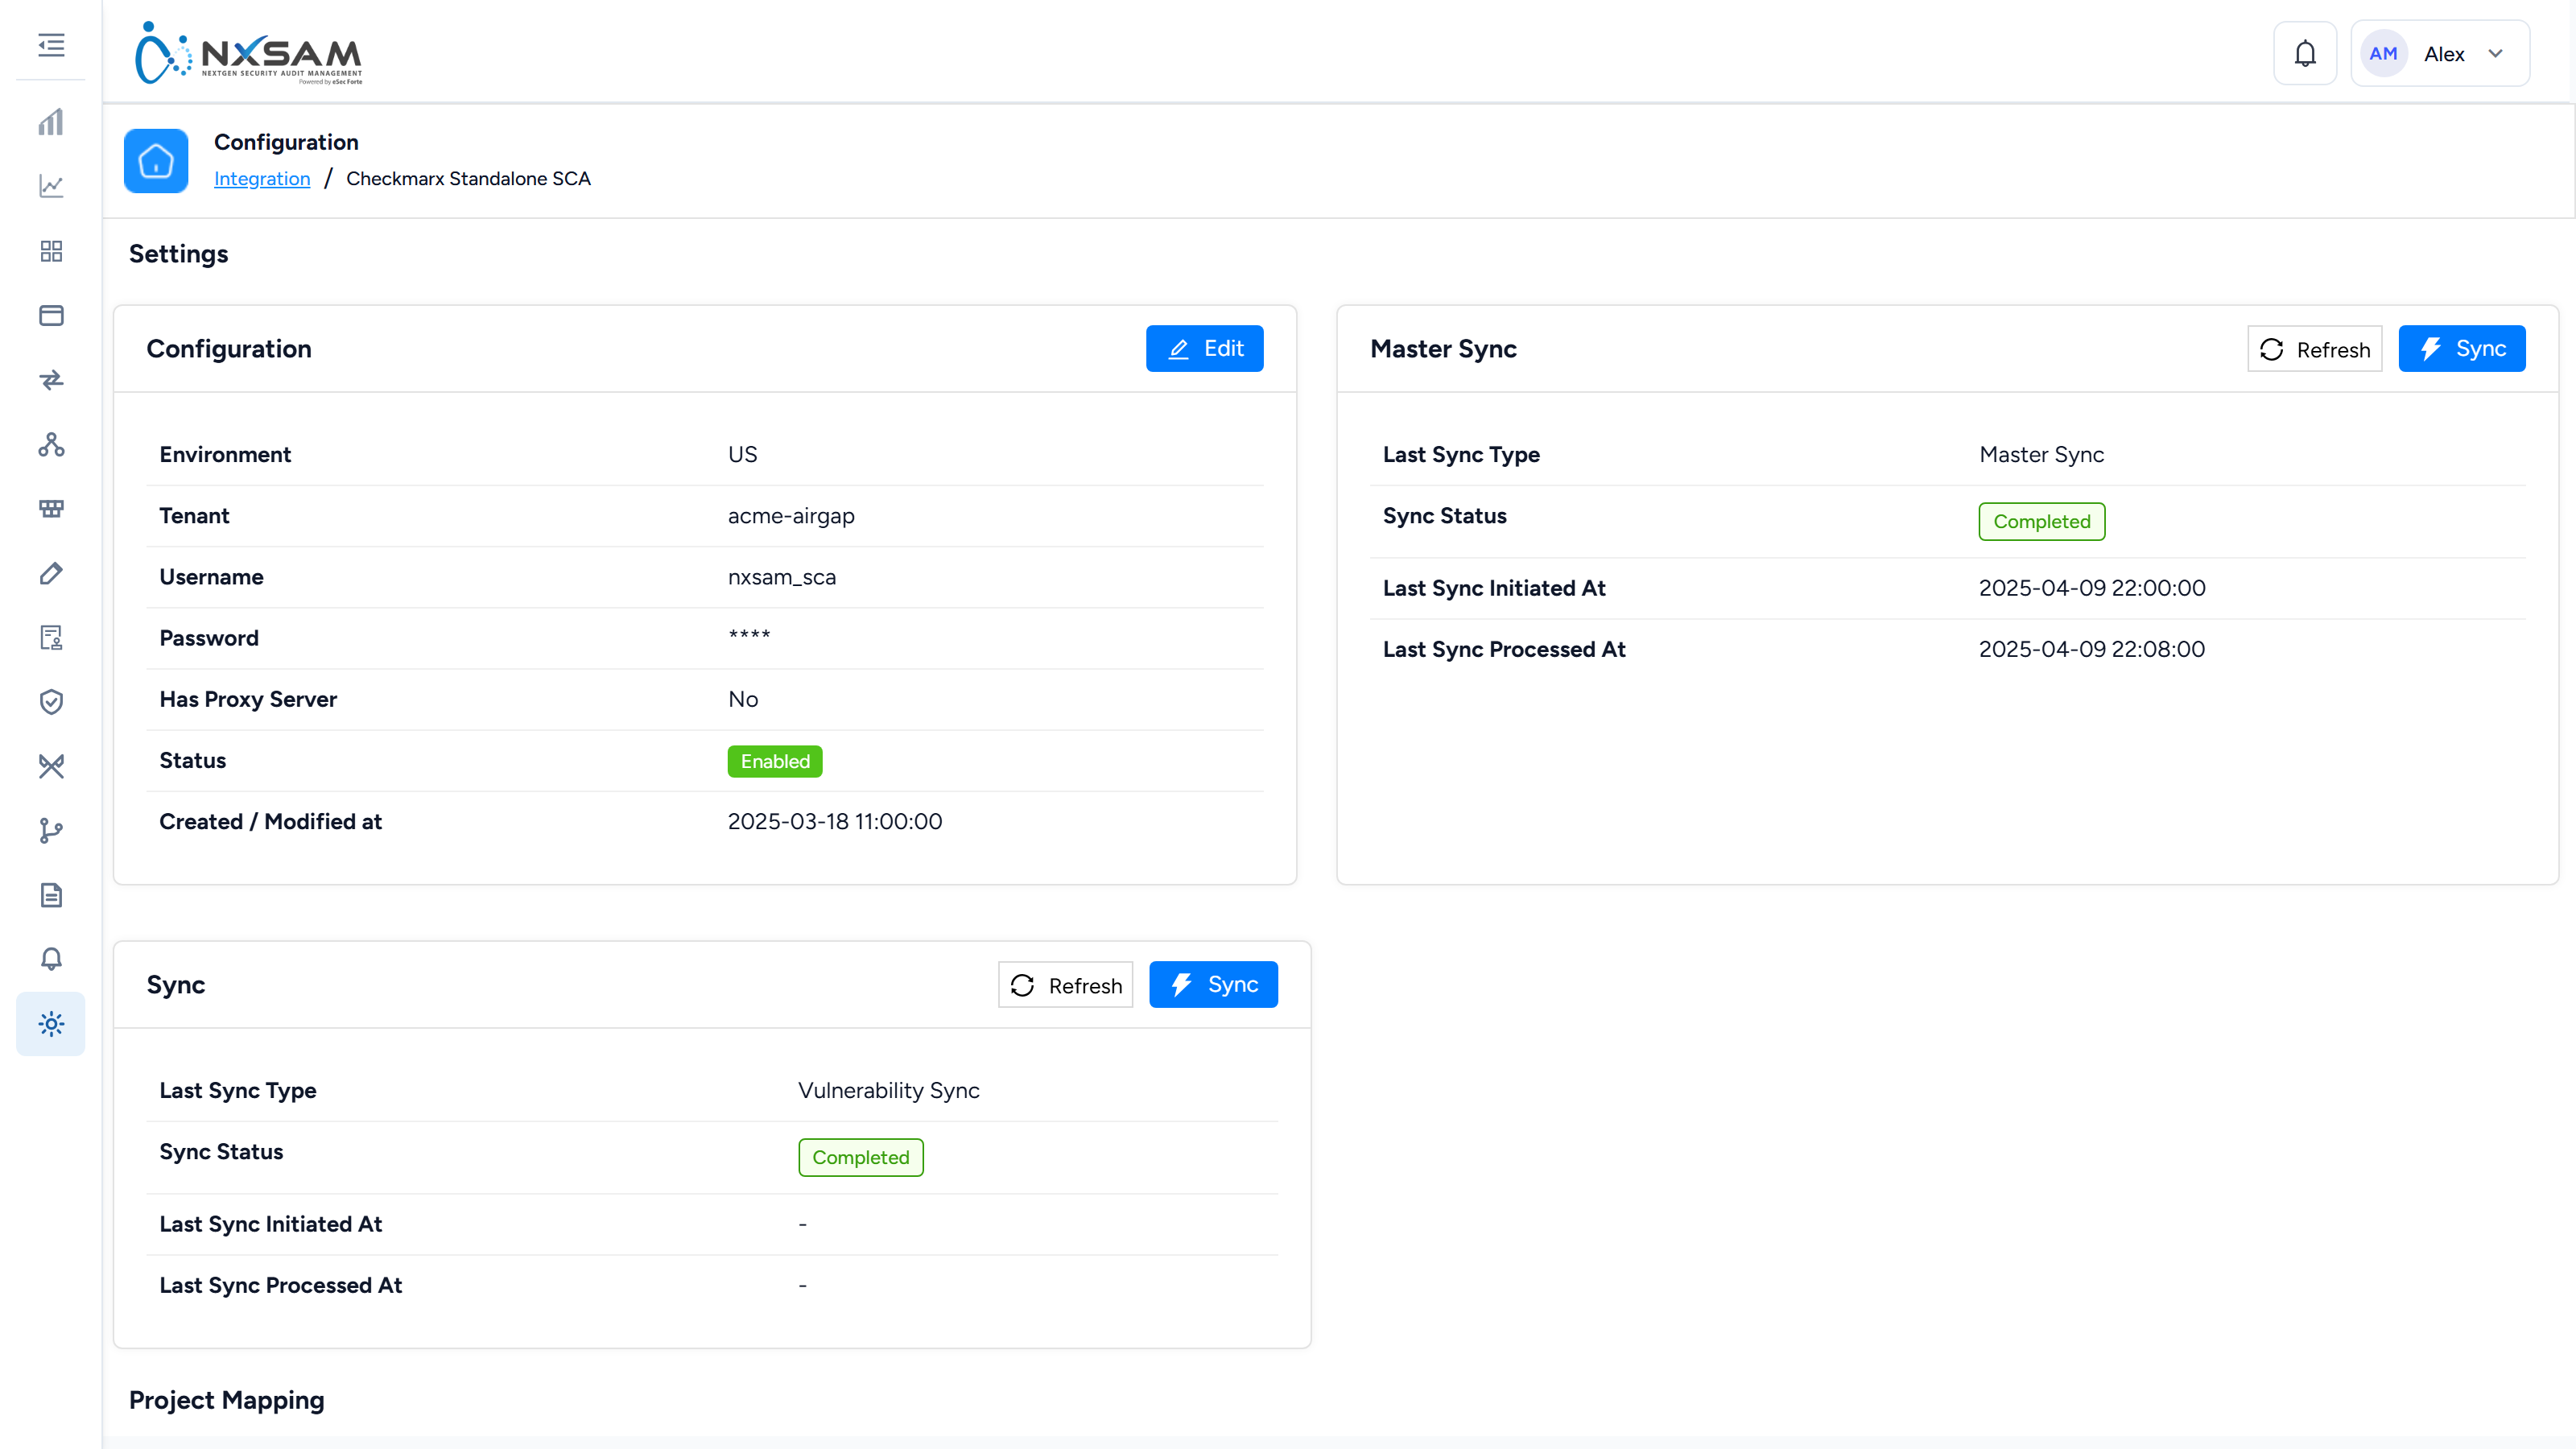
Checkmarx Standalone SCA
SCA run independently of the main Checkmarx platform.
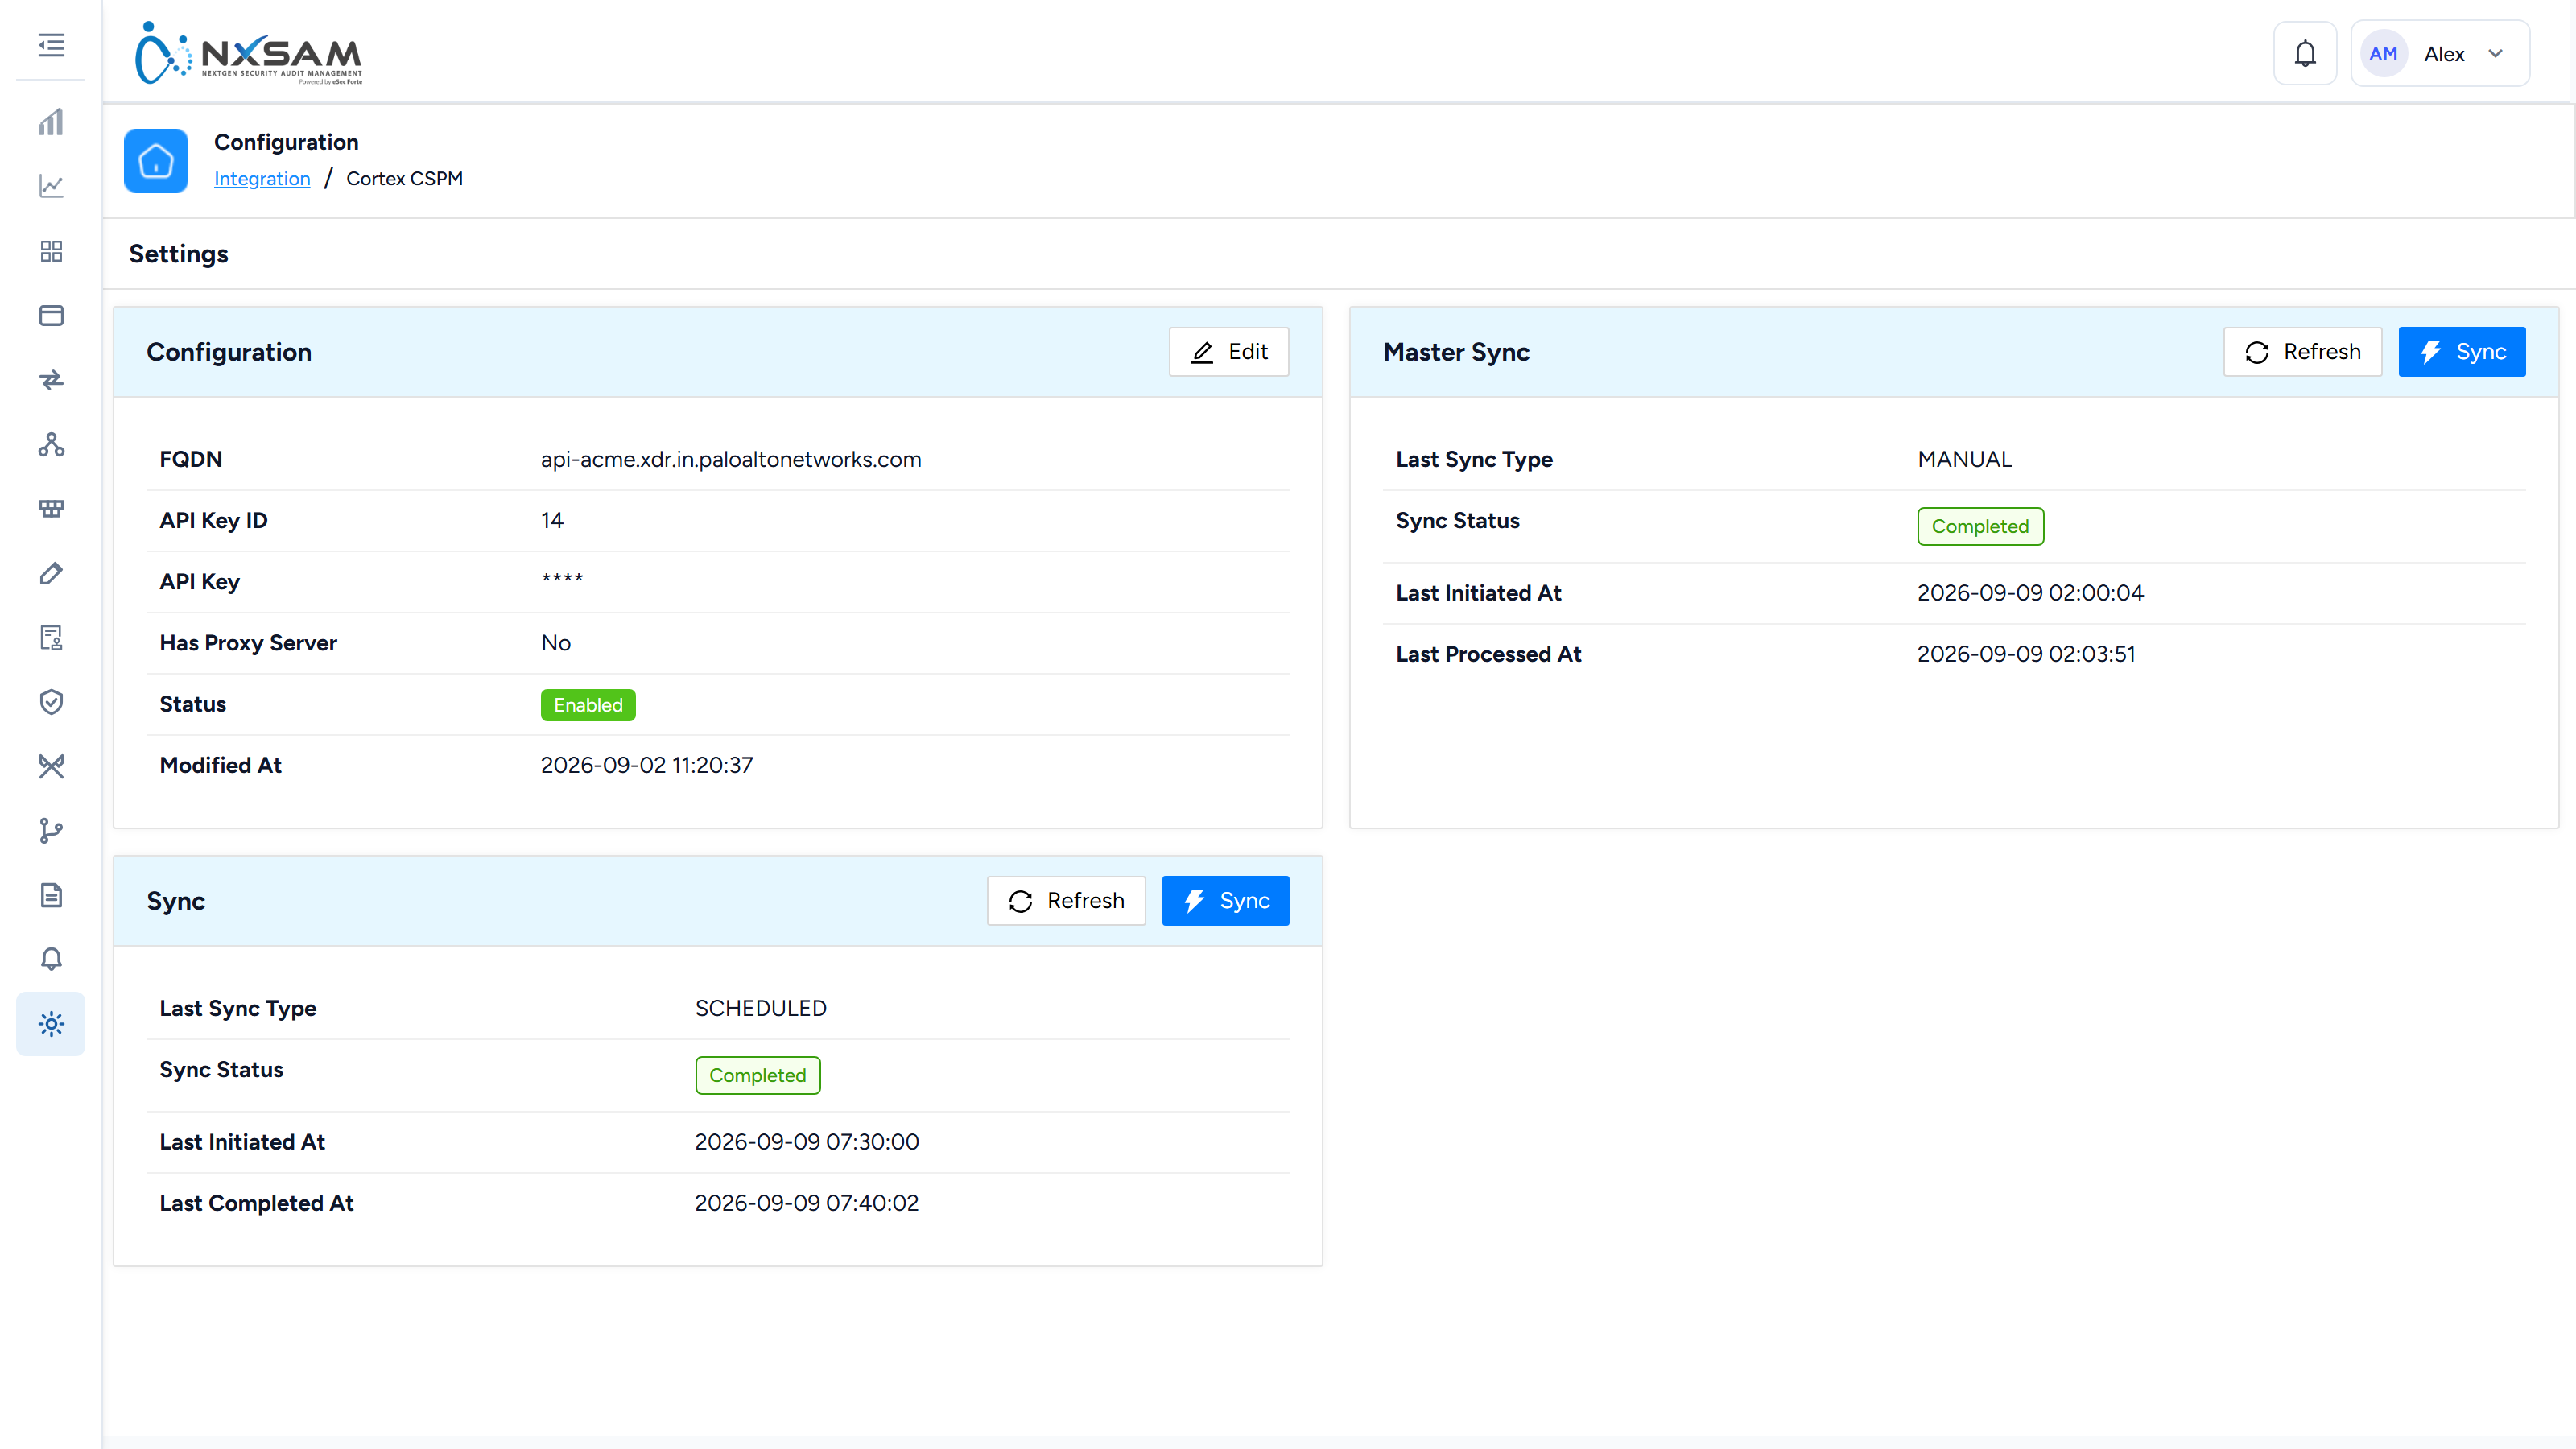
Cortex CSPM
Palo Alto's posture platform, feeding the CSPM screens rather than the Prisma ones. Master Sync brings rules and policies; Sync brings assets, issues and cases against them — in that order.
Cortex XDR
Host insight findings as a Network VA source. Shown here in its unconfigured state.
Dependency Track
Continuous composition analysis from an SBOM rather than from a scan.
Fortify
Static application security testing.
Gitleaks
Secrets detection — credentials committed into source control.
JFrog Xray
Composition analysis over artefacts held in Artifactory.
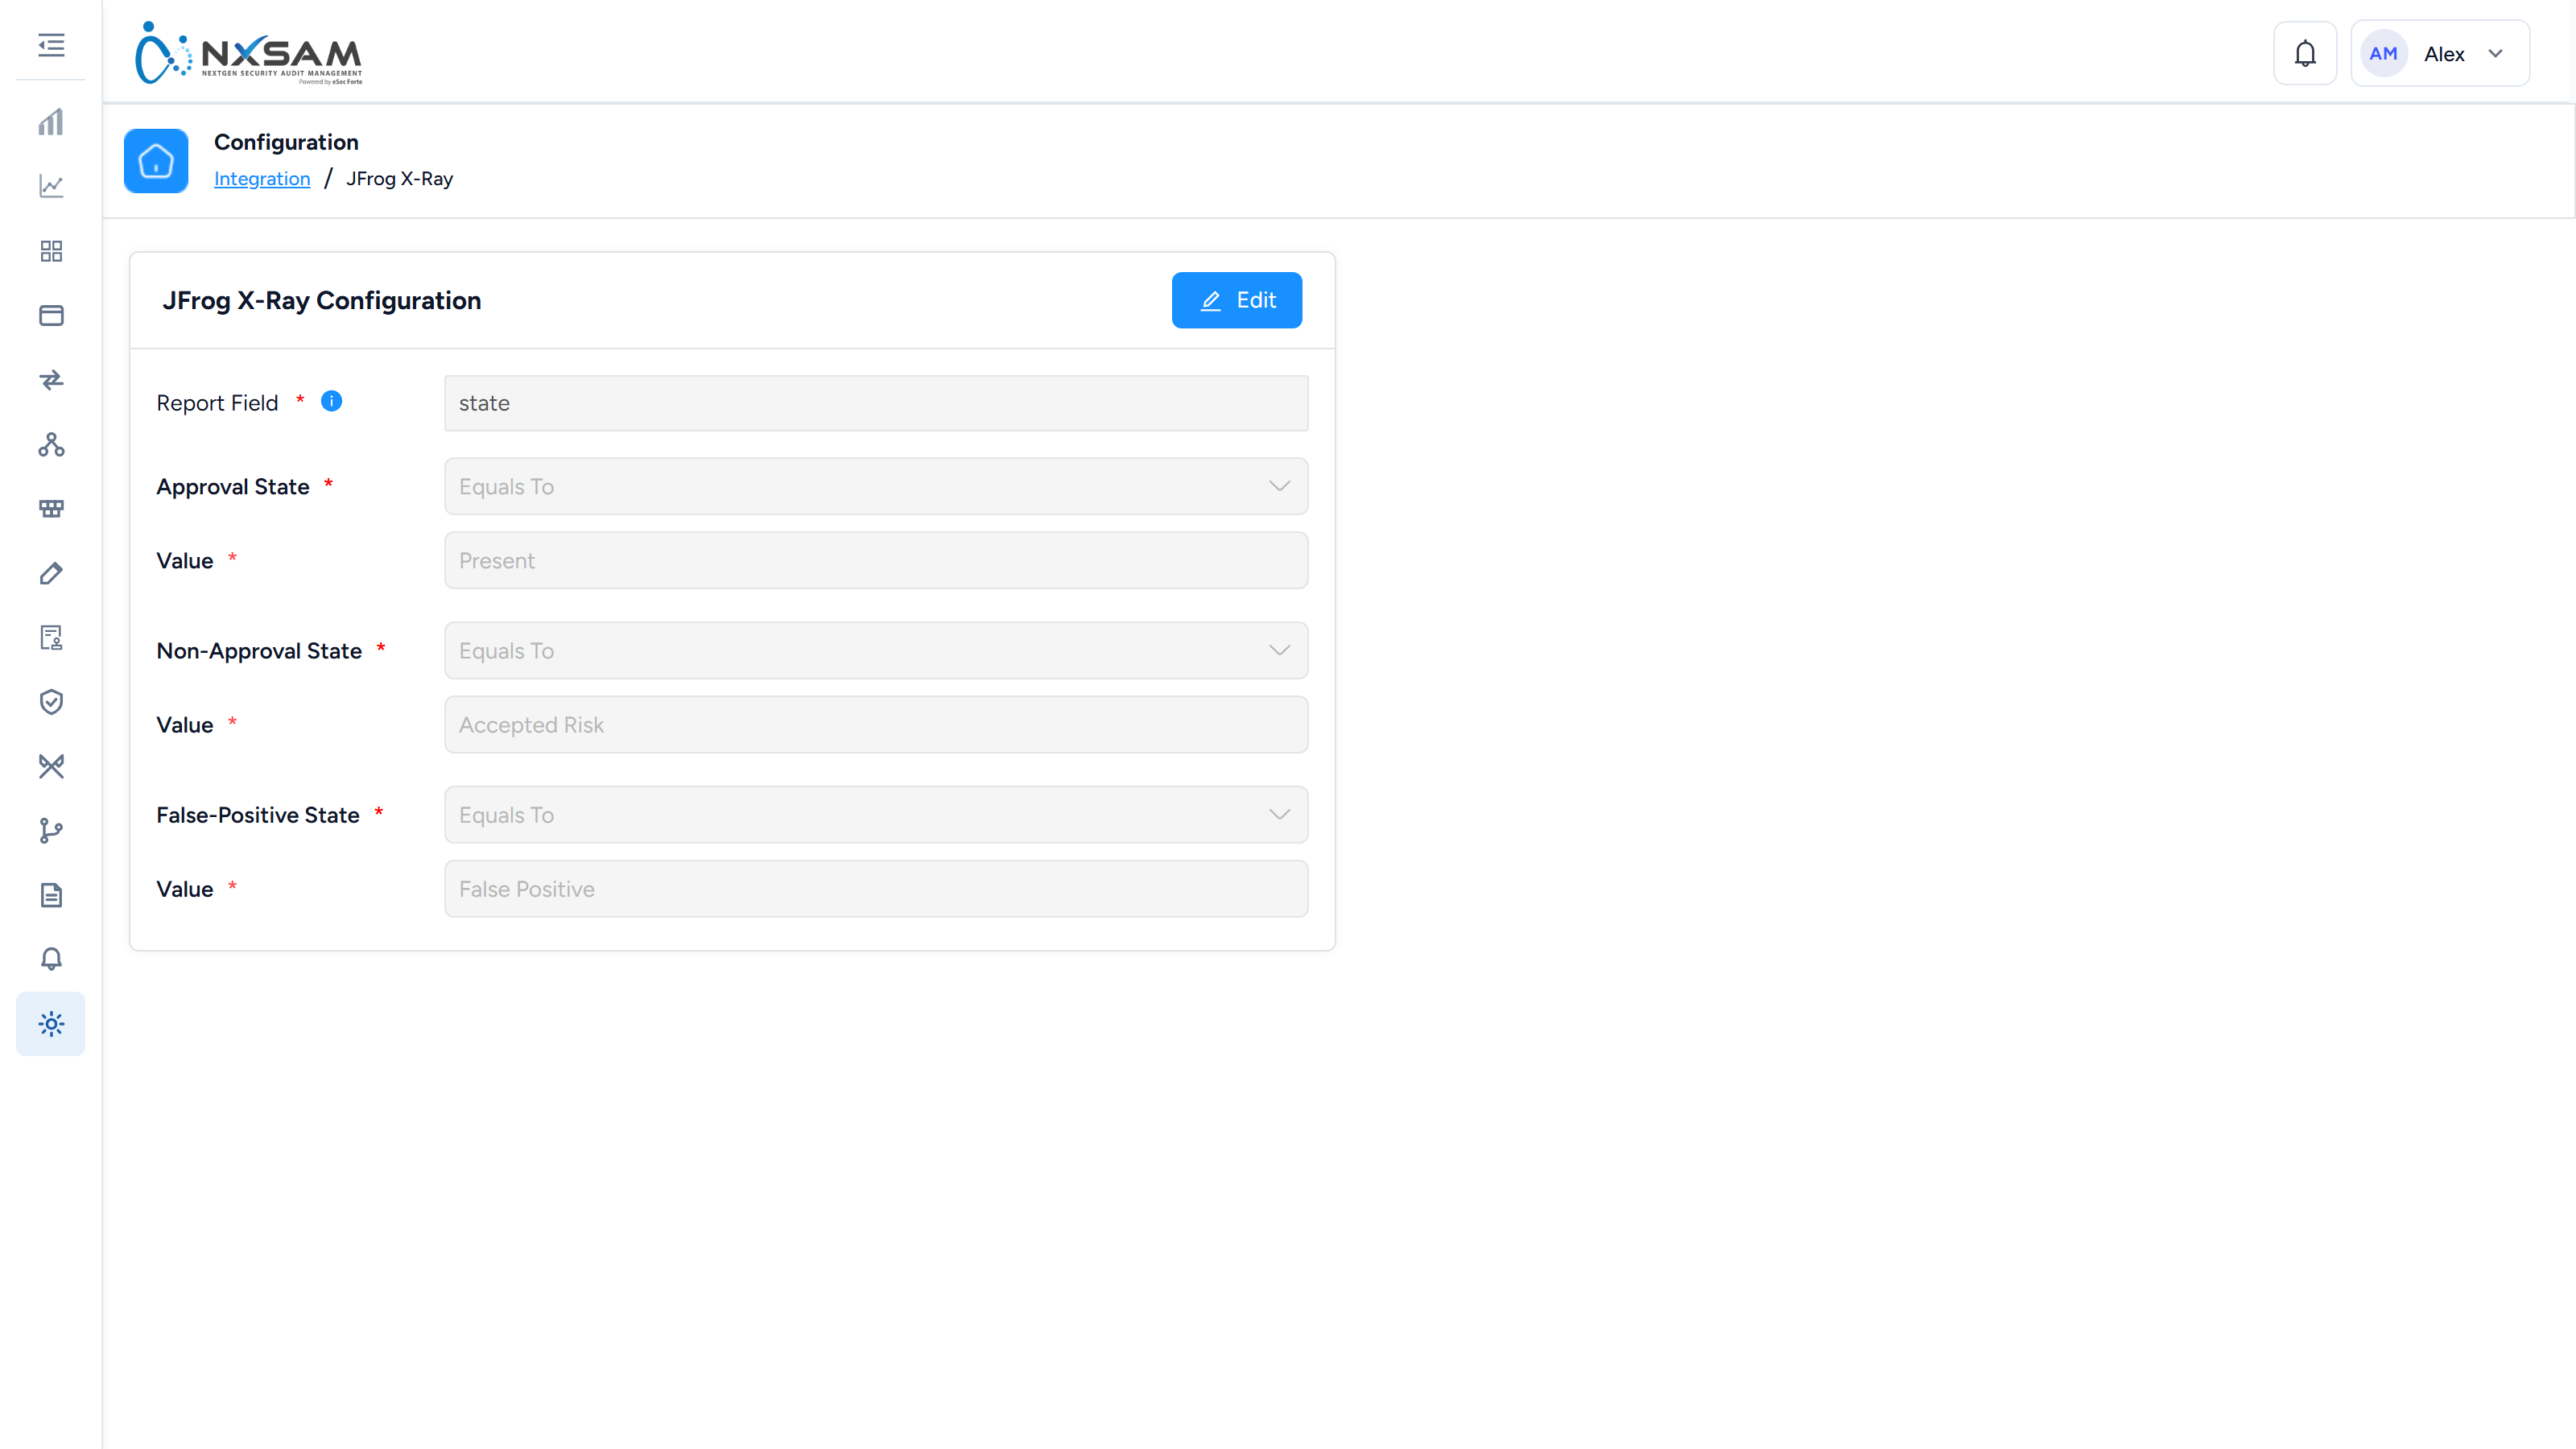
Netsparker
Dynamic application scanning.
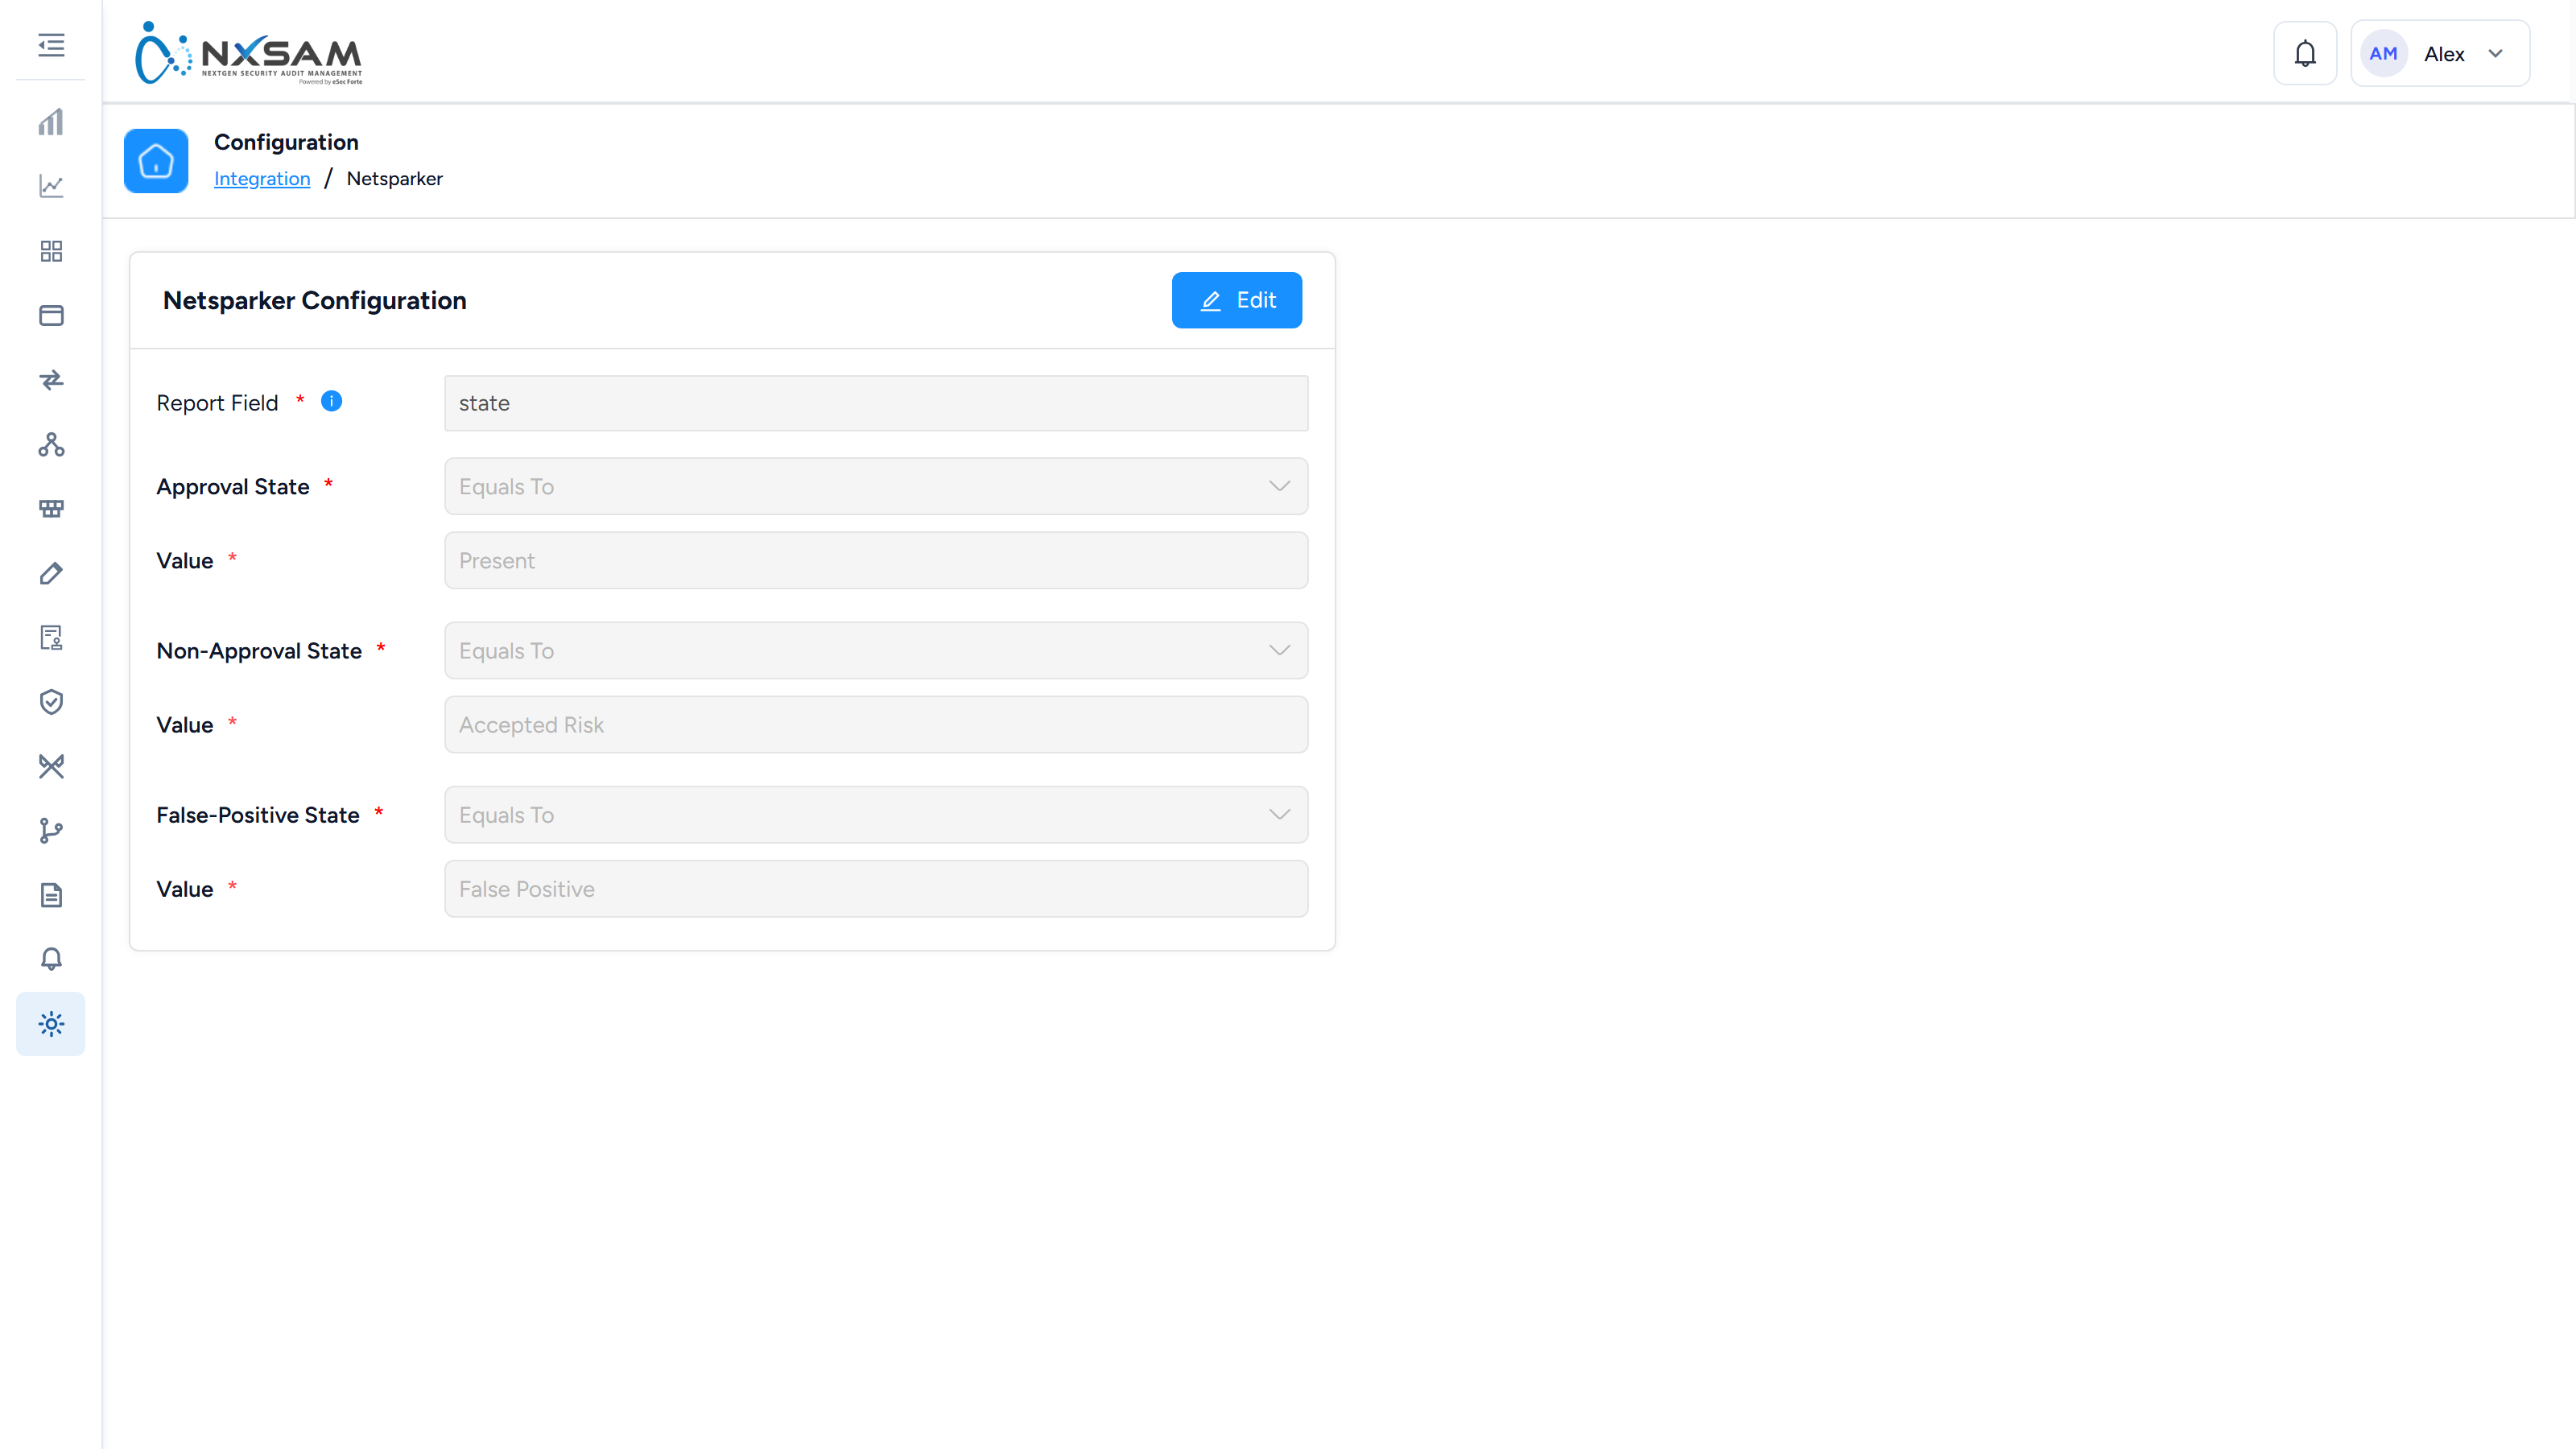
Nexpose Upload Mapping
Which column of a Nexpose export carries each date NxSAM needs, and whether it is mandatory.
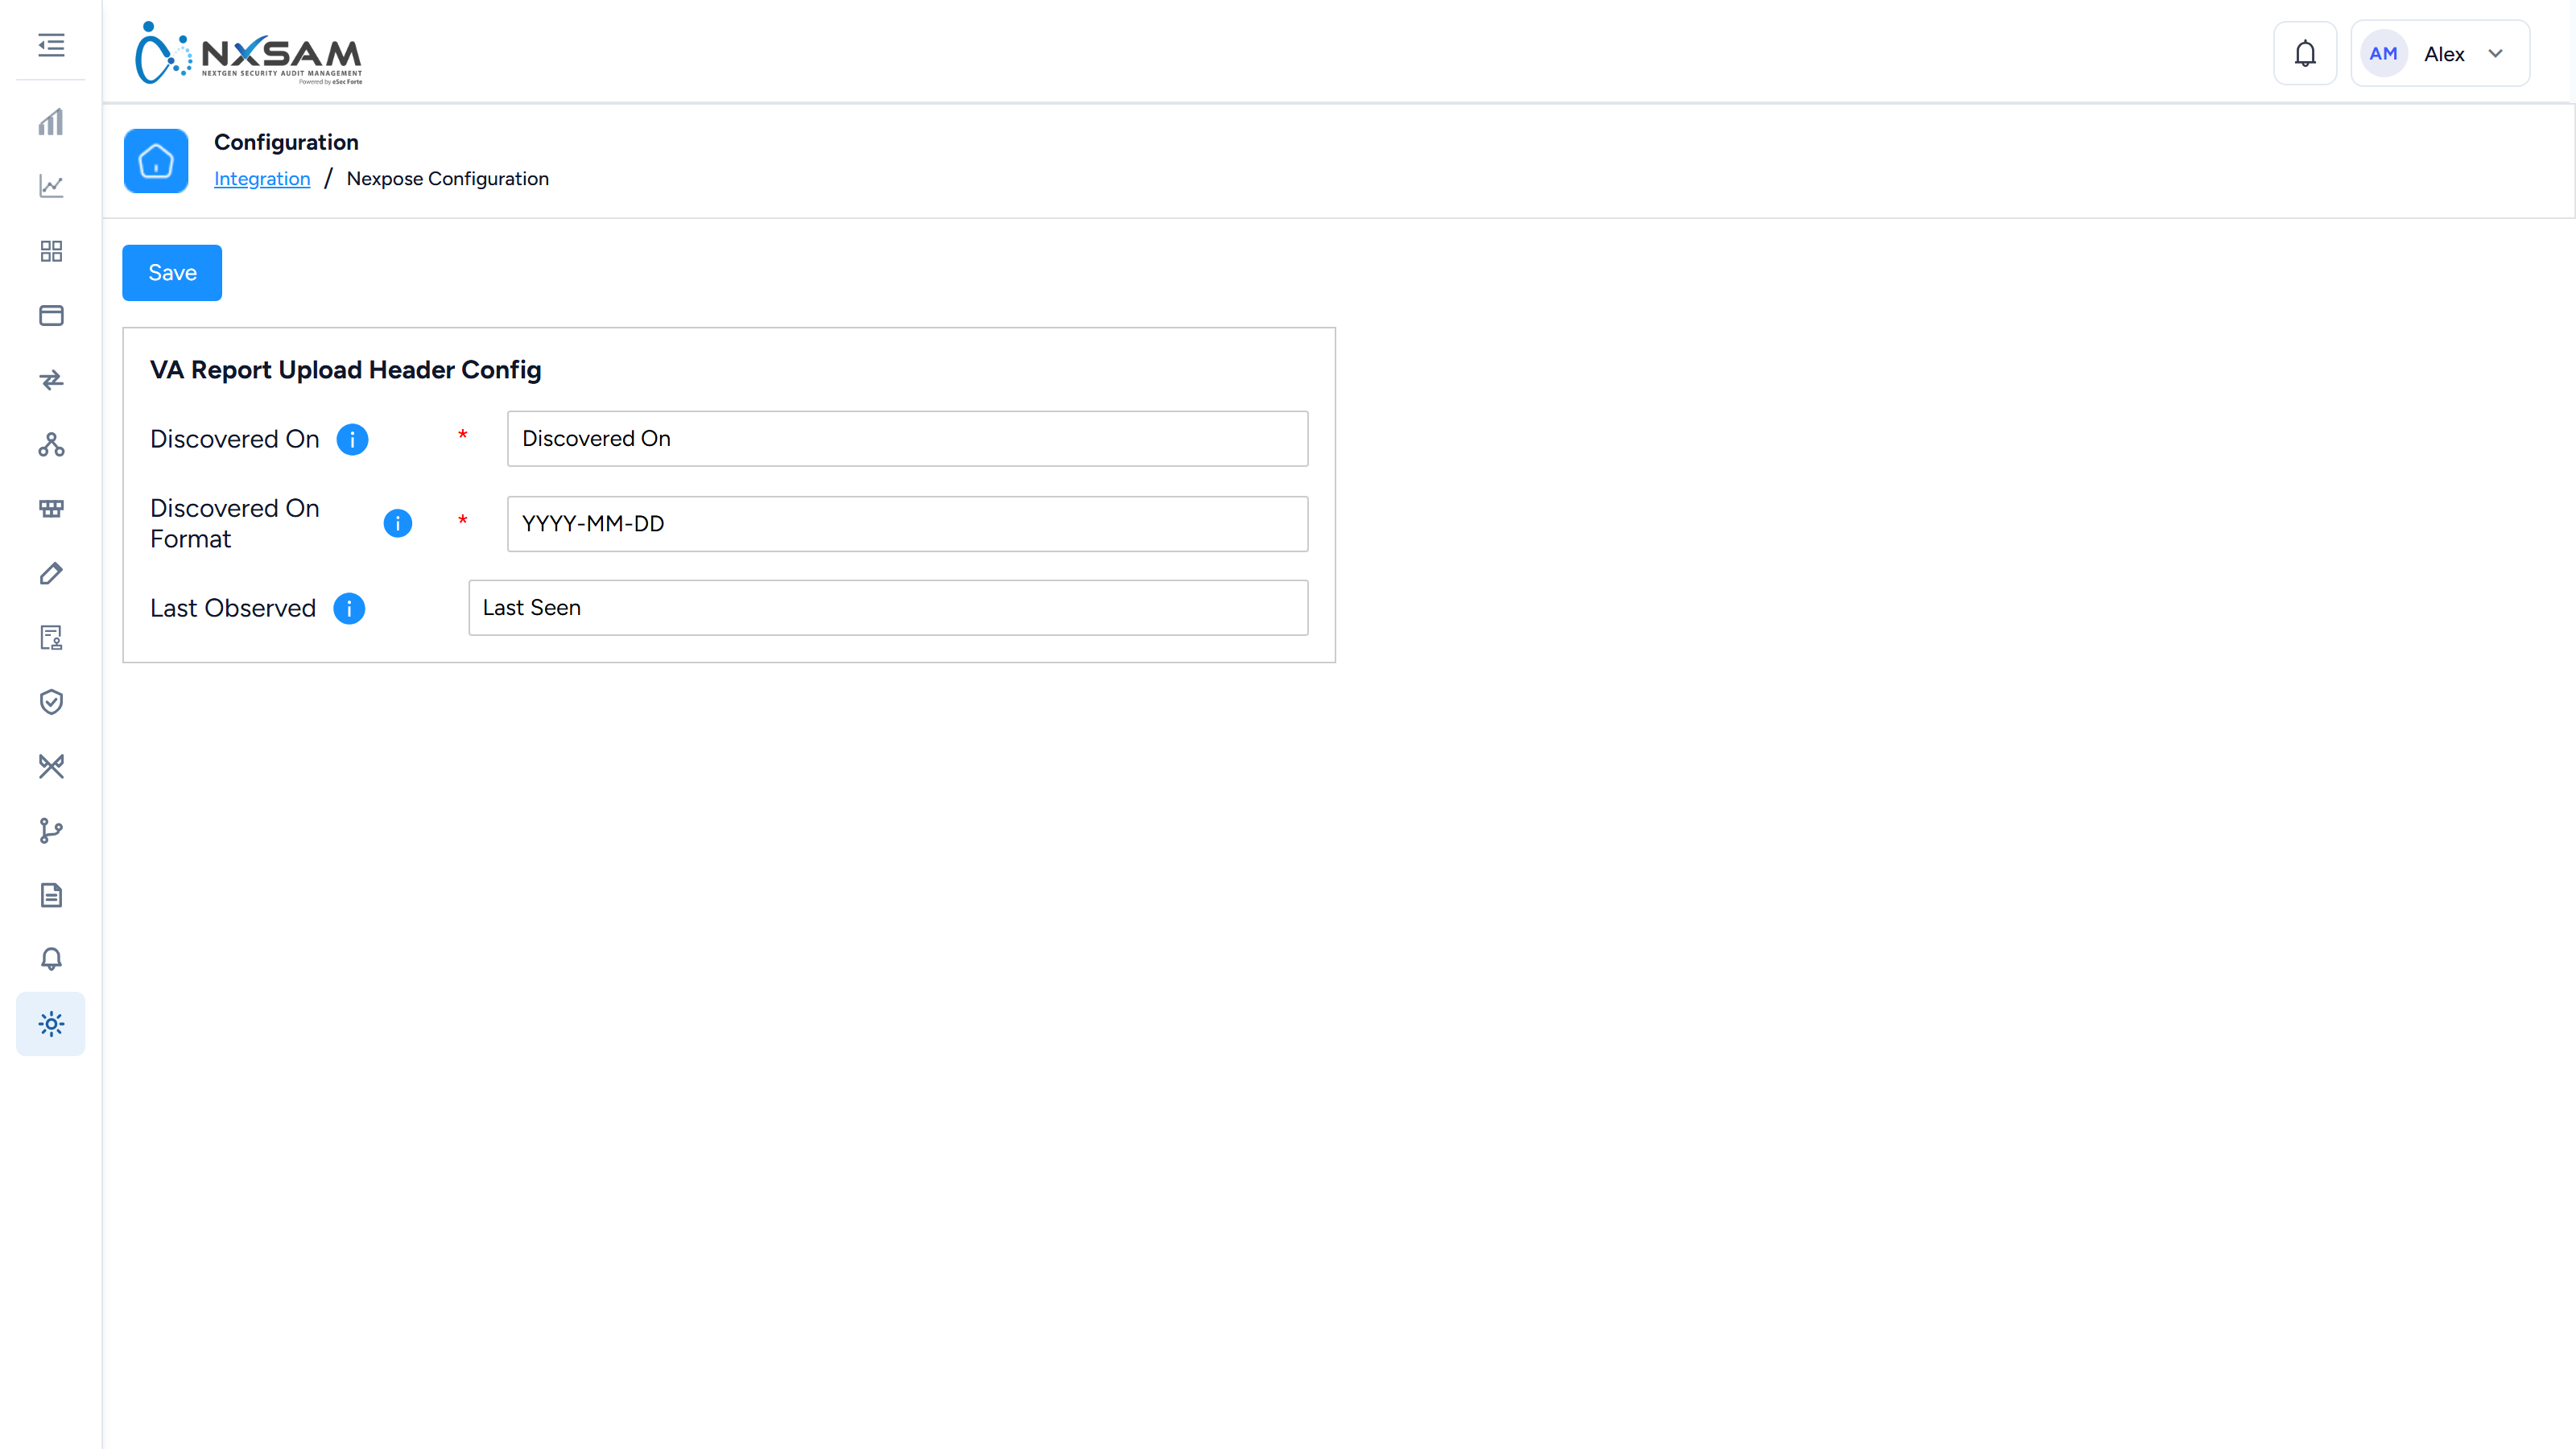
Prisma Cloud
Container security. Connects to the registry scan results and the collections they belong to.
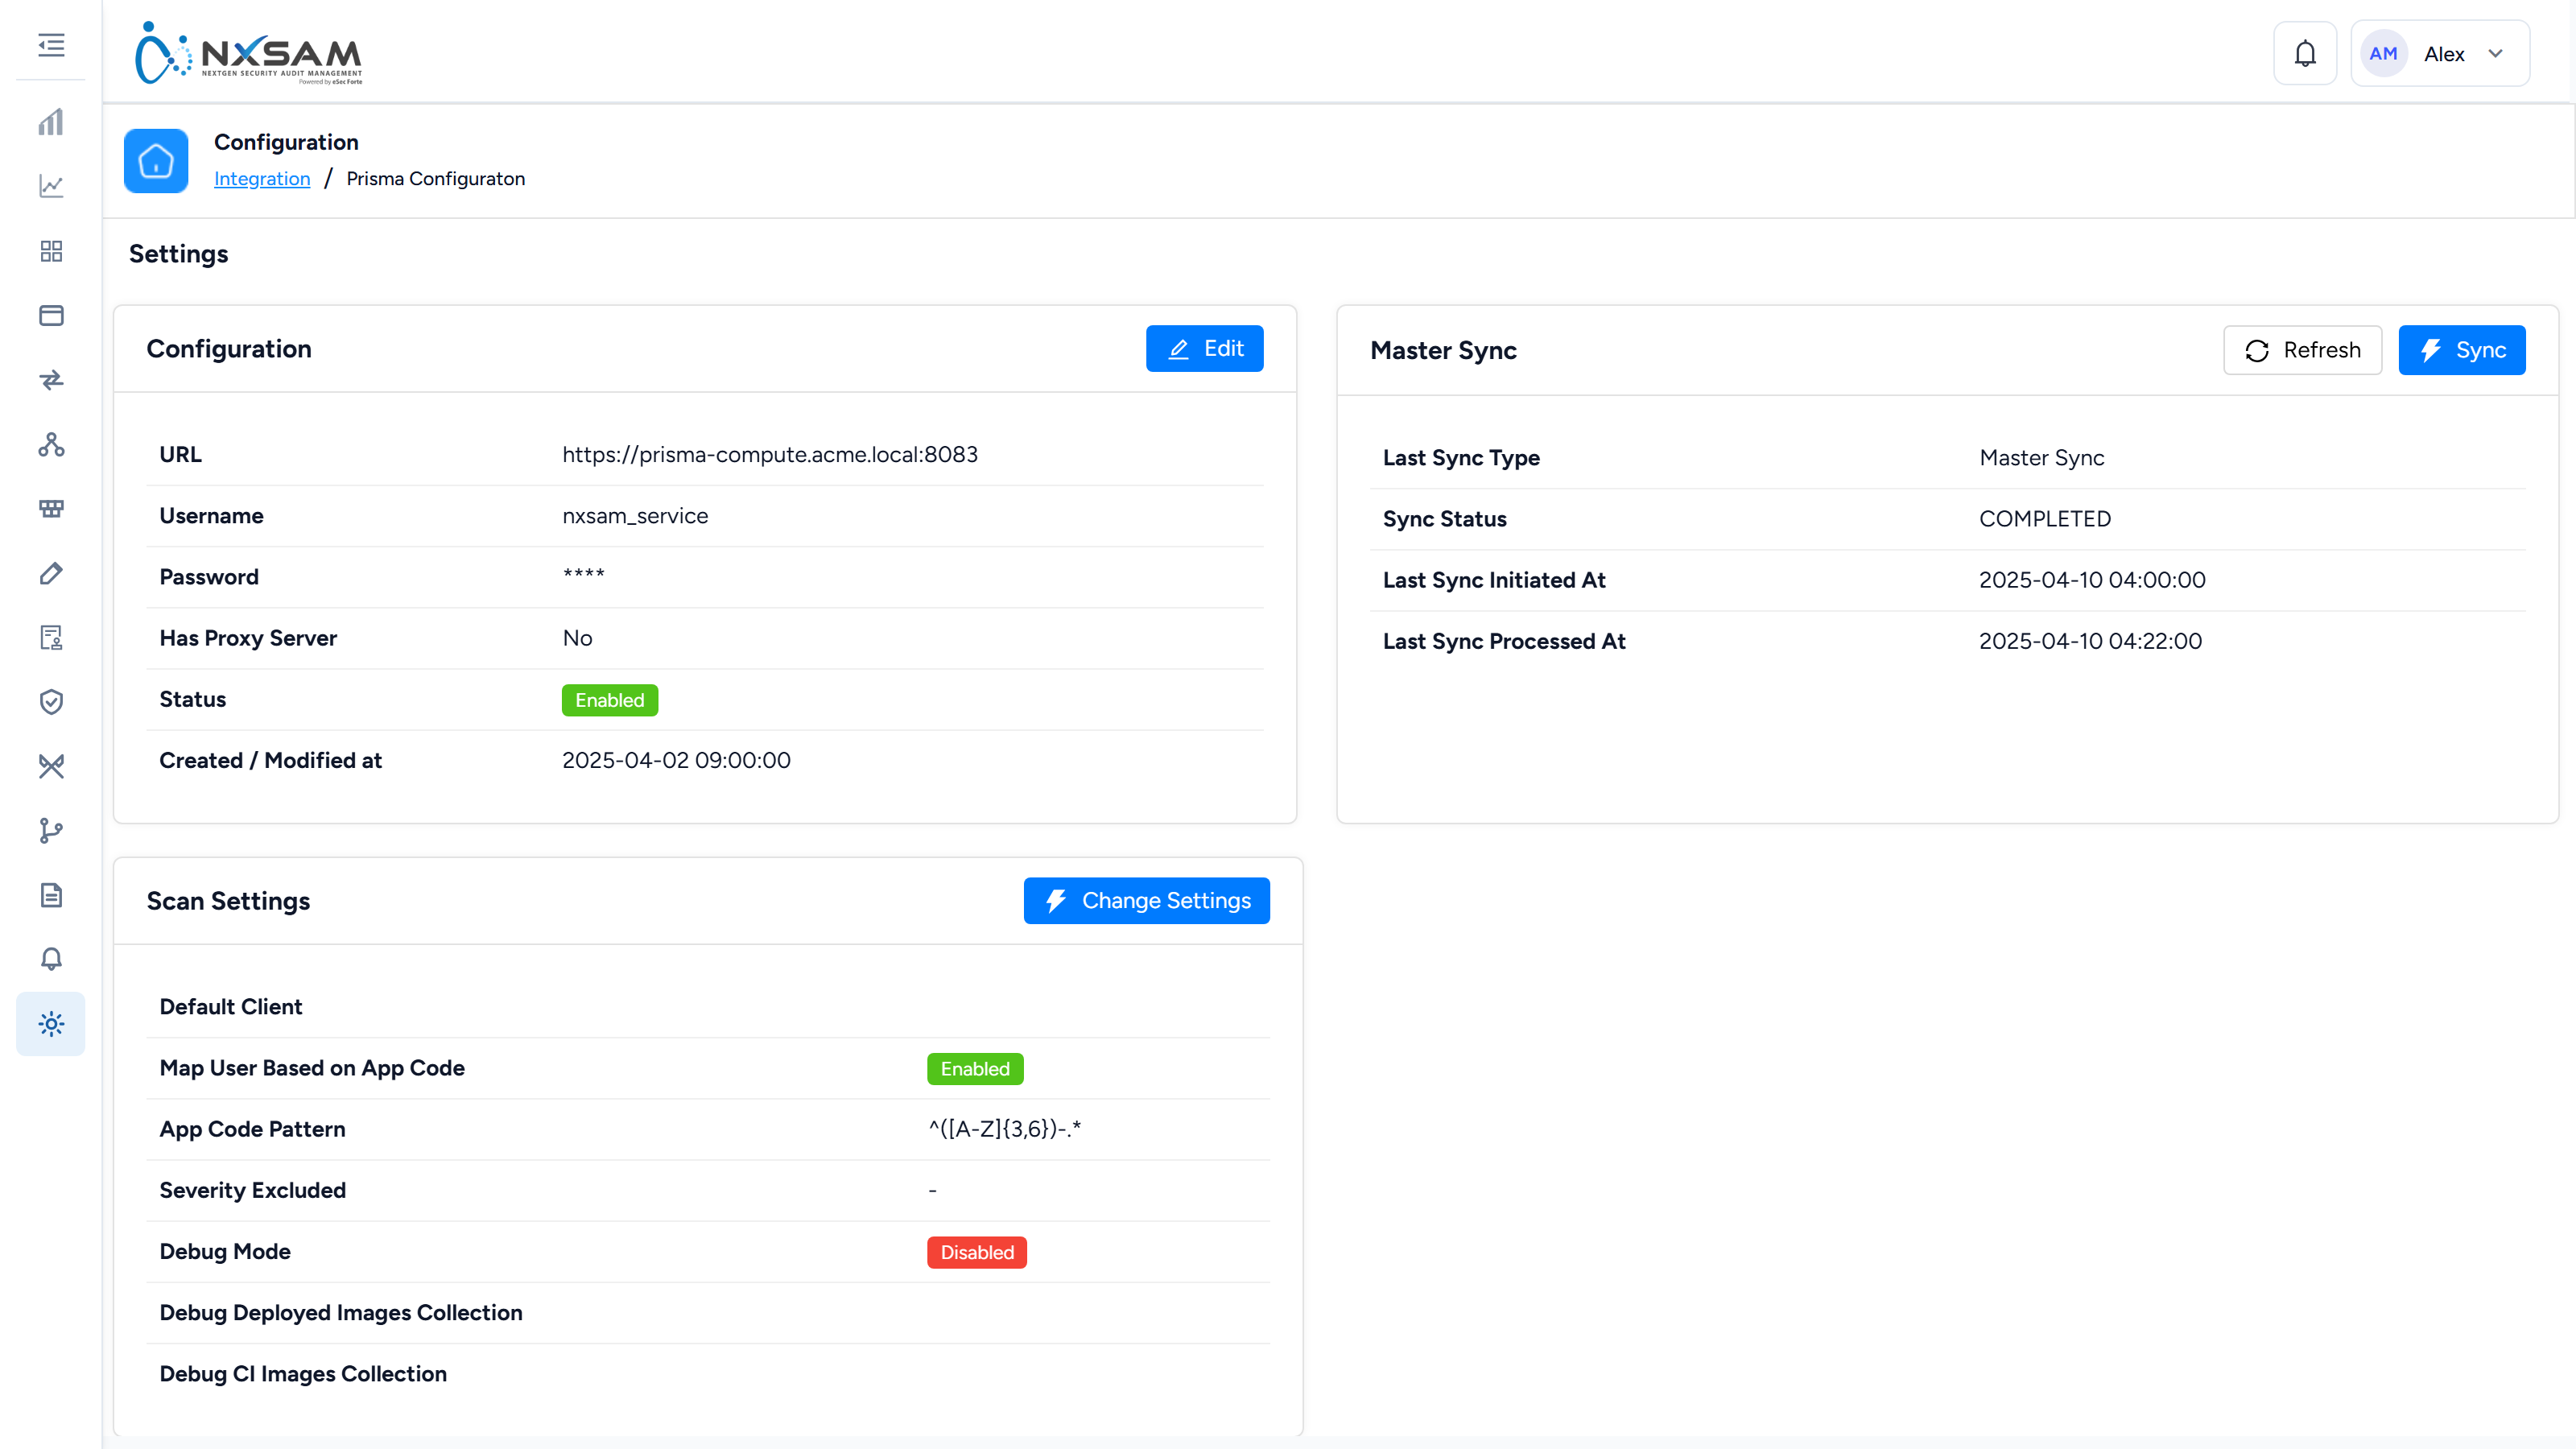
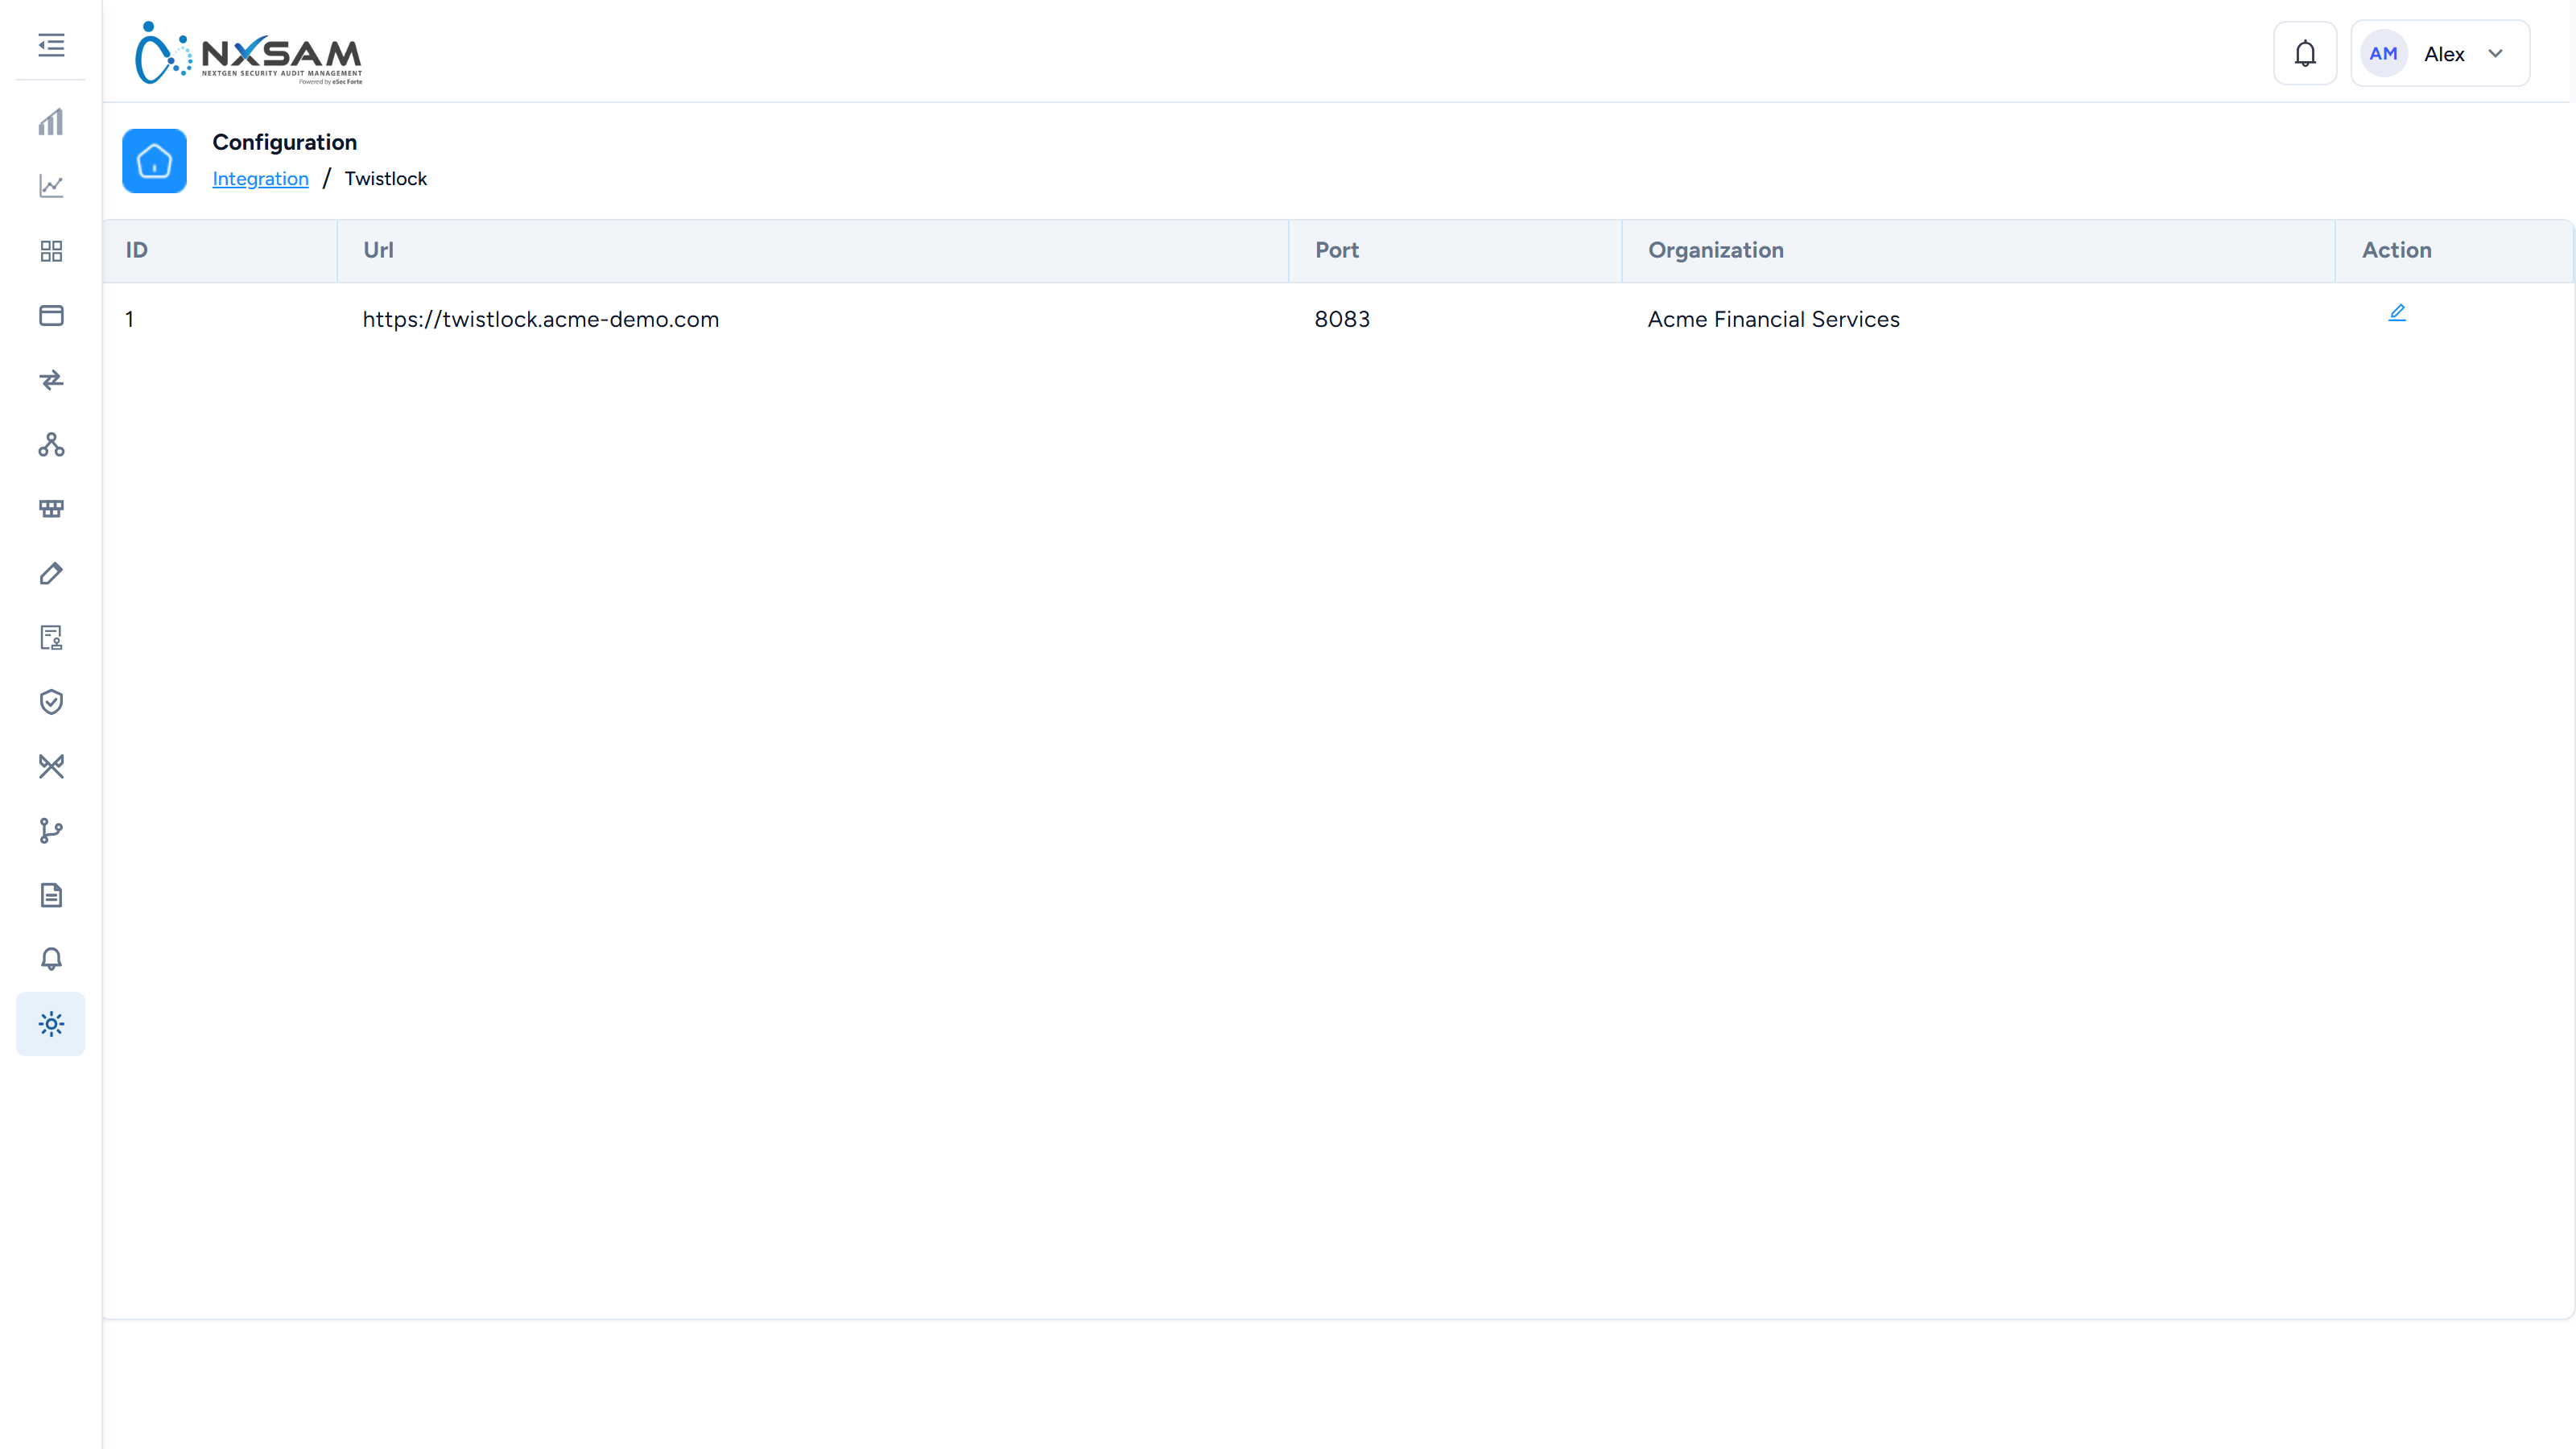
Prisma Cloud (Twistlock) Connection
The connection to the container scanner: endpoint, port and credentials.
Prisma Cloud CSPM
Cloud posture. Separate from the container integration even though the vendor is the same.
SentinelOne CSPM
An alternative cloud posture source, feeding the CSPM screens. One Data Sync brings everything.
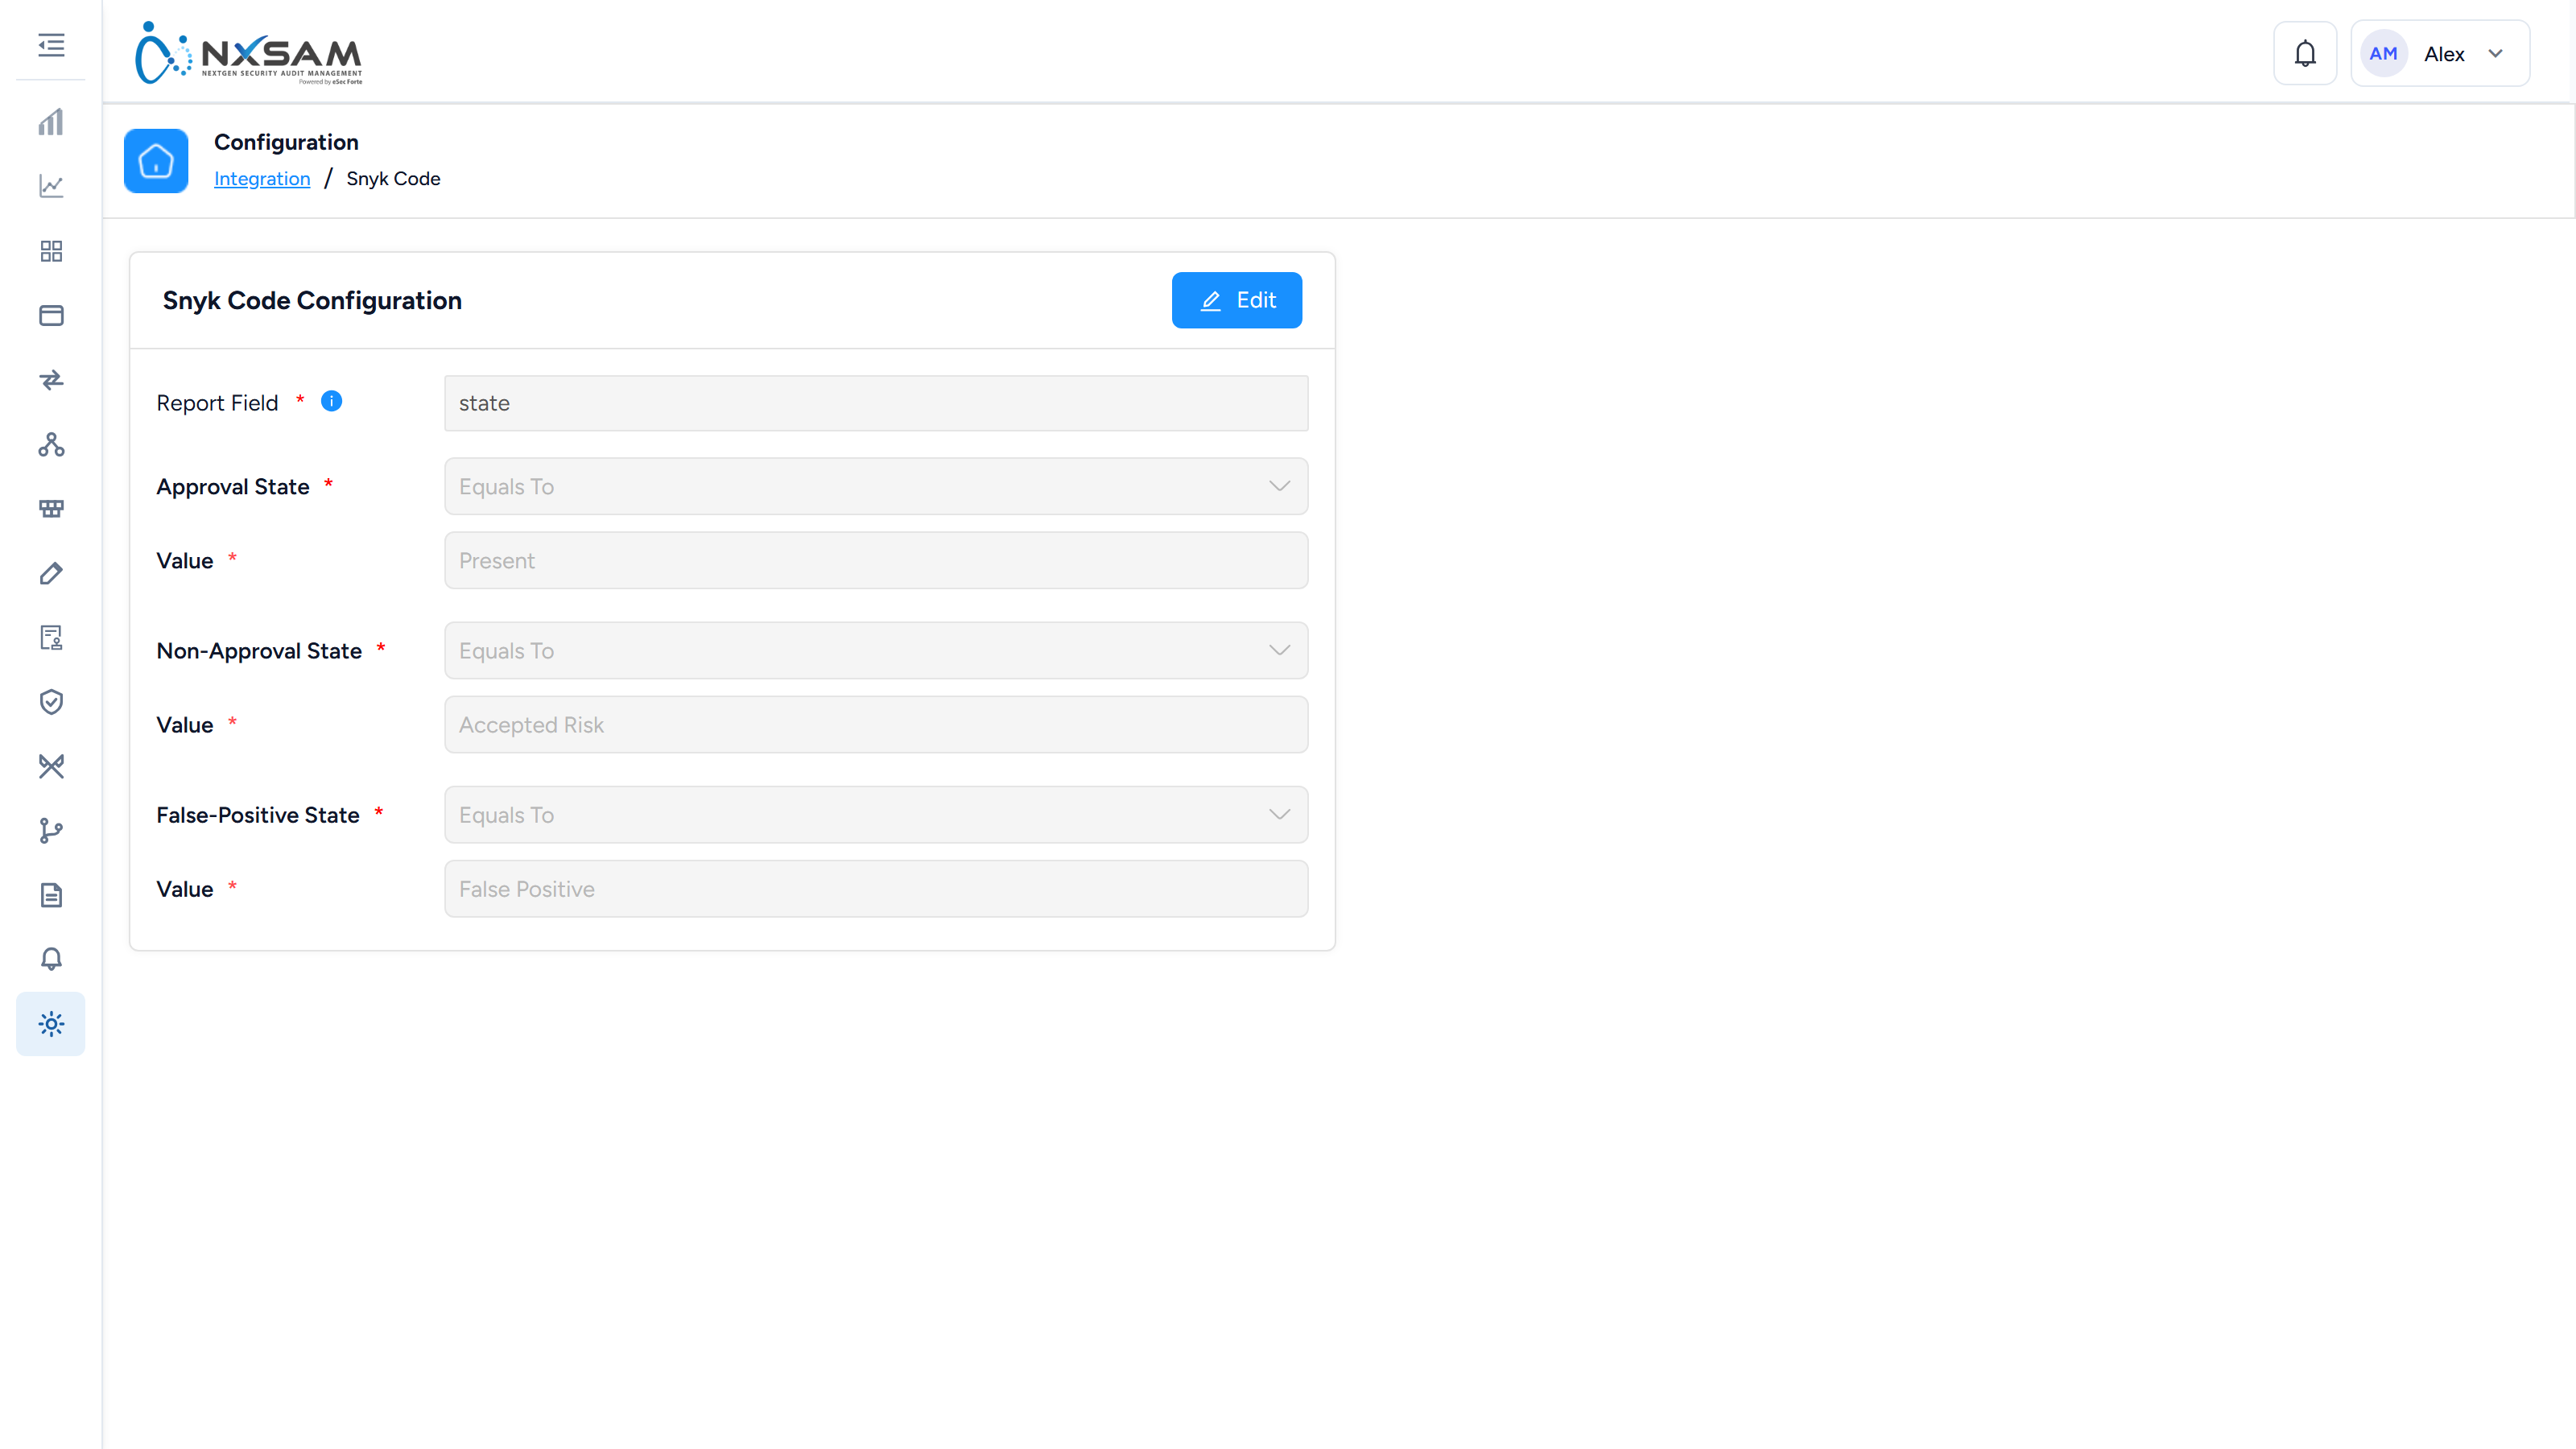
Snyk Code
Static analysis of source code.
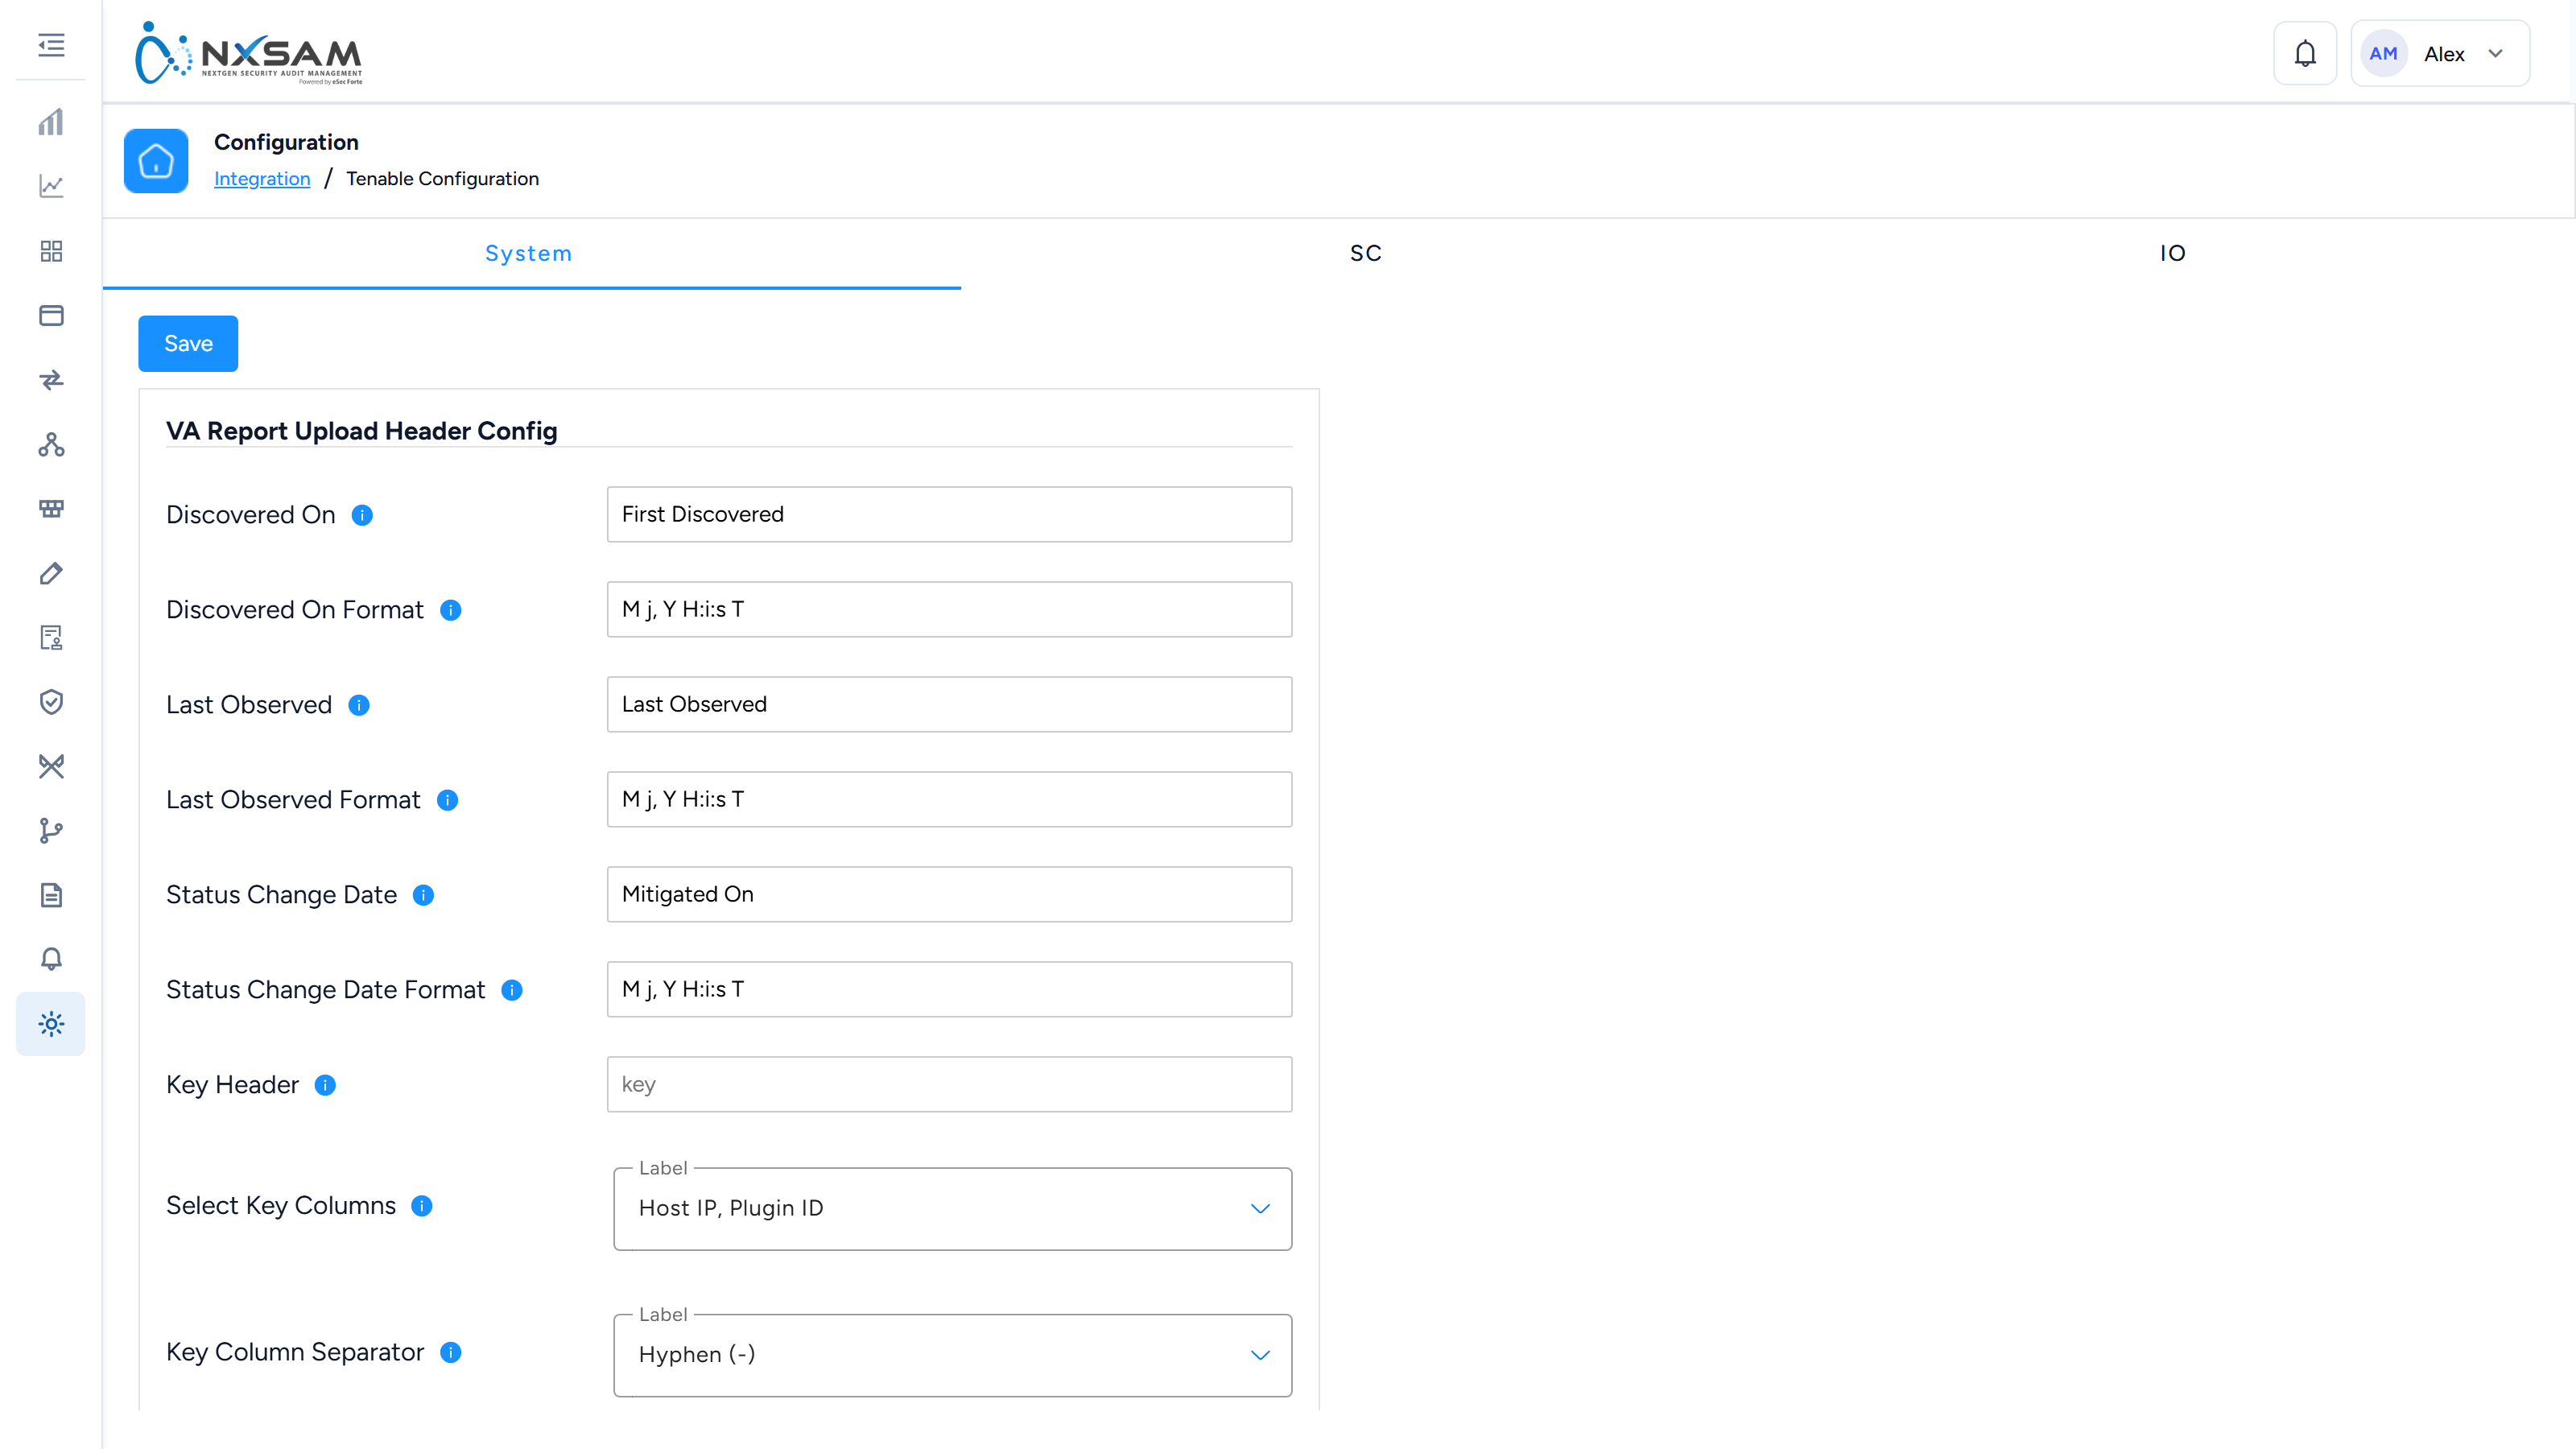
Tenable
Network VA. Credentials, plus the column mapping that decides how the report's dates and keys are read.
Vulnerability Mapping — Checkmarx
How this tool's identifiers line up with the catalogue, so the same weakness from two tools is one finding rather than two.